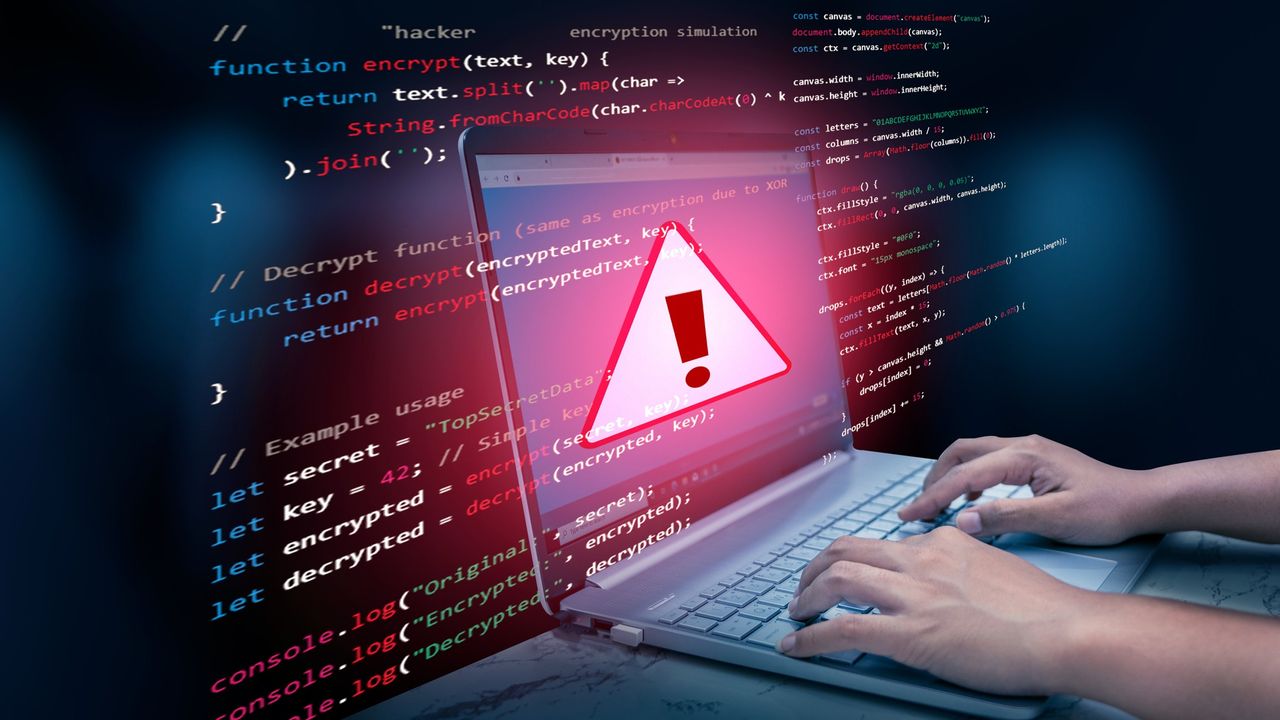
- OpenCart websites were silently injected with malware that mimics trusted tracking scripts
- Script hides in analytics tags and quietly swaps real payment forms for fake ones
- Obfuscated JavaScript allowed attackers to slip past detection and launch credential theft in real time
A new Magecart-style attack has raised concerns across the cybersecurity landscape, targeting ecommerce websites which rely on the OpenCart CMS.