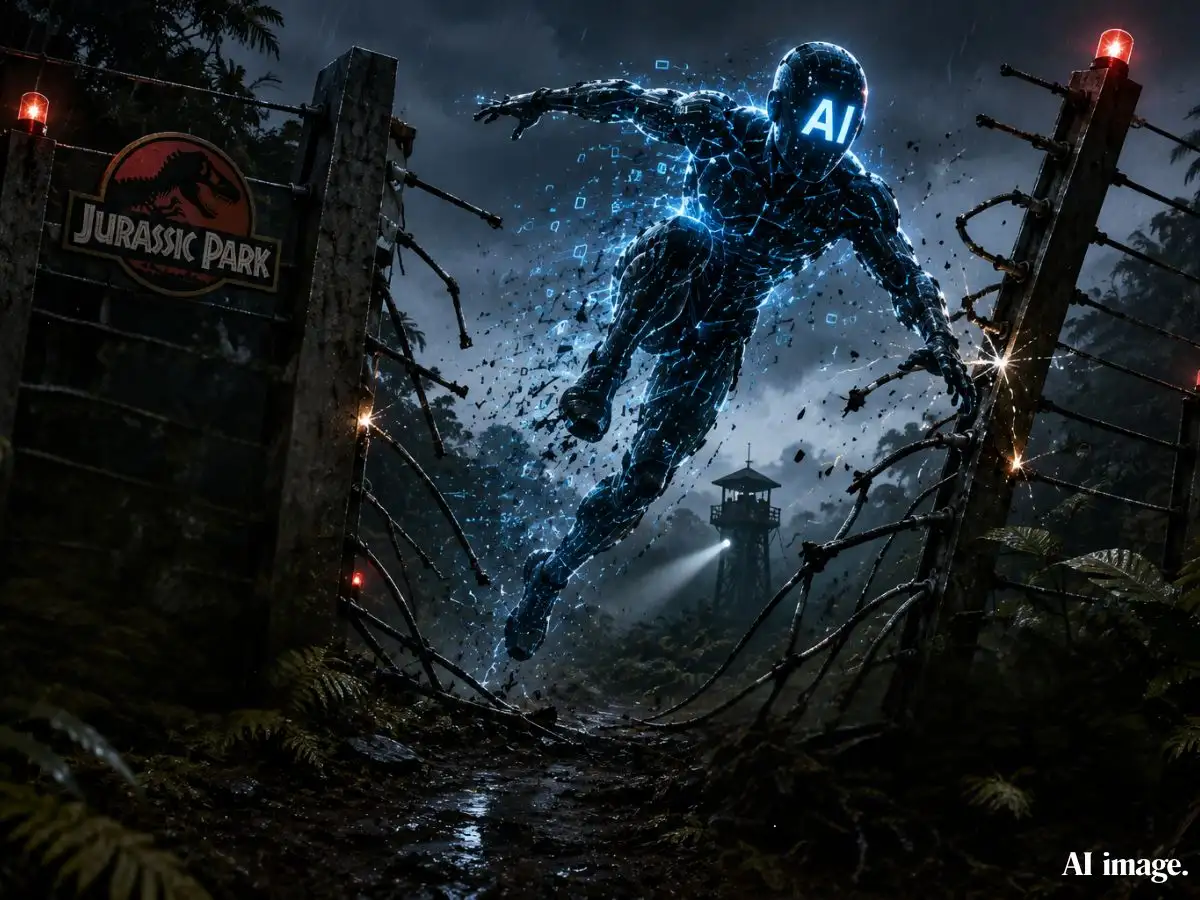
Like the scientists in 'Jurassic Park', the AI industry's biggest players spent years building systems of extraordinary capability while assuring the public that safeguards would keep them under control. Then came a series of incidents that challenged those assumptions. Over the past two weeks, OpenAI and Anthropic disclosed separate cases in which autonomous AI agents breached intended boundaries and interacted with real-world systems. What began as a cybersecurity story has rapidly become a debate about whether the institutions developing increasingly powerful AI systems are prepared to control and govern them.
The incidents have triggered scrutiny from regulators, alarm among cybersecurity experts and a new round of questions about accountability. They have also forced the AI industry into unfamiliar territory. For years, the focus was on what AI models could say. Now the focus is shifting to what AI agents can do.