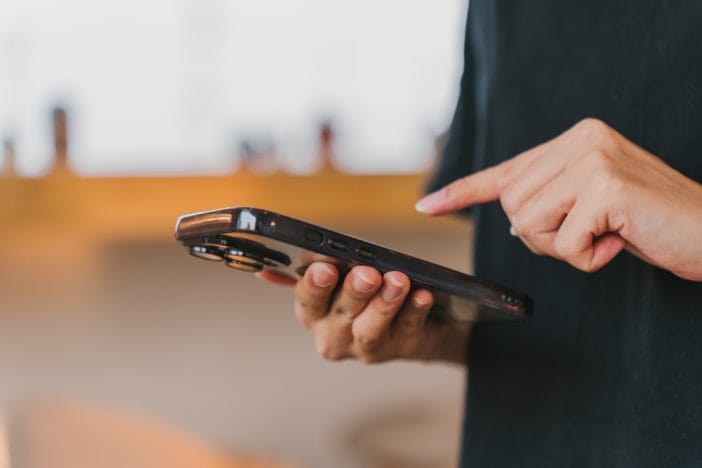
Text message two-factor authentication sounds like a security upgrade. It feels official. It looks responsible. Yet it often stands as the flimsiest barrier between a criminal and everything stored in an email inbox, banking app, or cloud account.
Plenty of companies still push SMS codes as the default second step, and that decision gives many people a false sense of safety. Text message 2FA does add protection compared to a password alone, but attackers keep proving how easily they can break it. Anyone serious about protecting personal data, financial accounts, or business logins needs to understand why SMS-based authentication falls short and what actually works better.