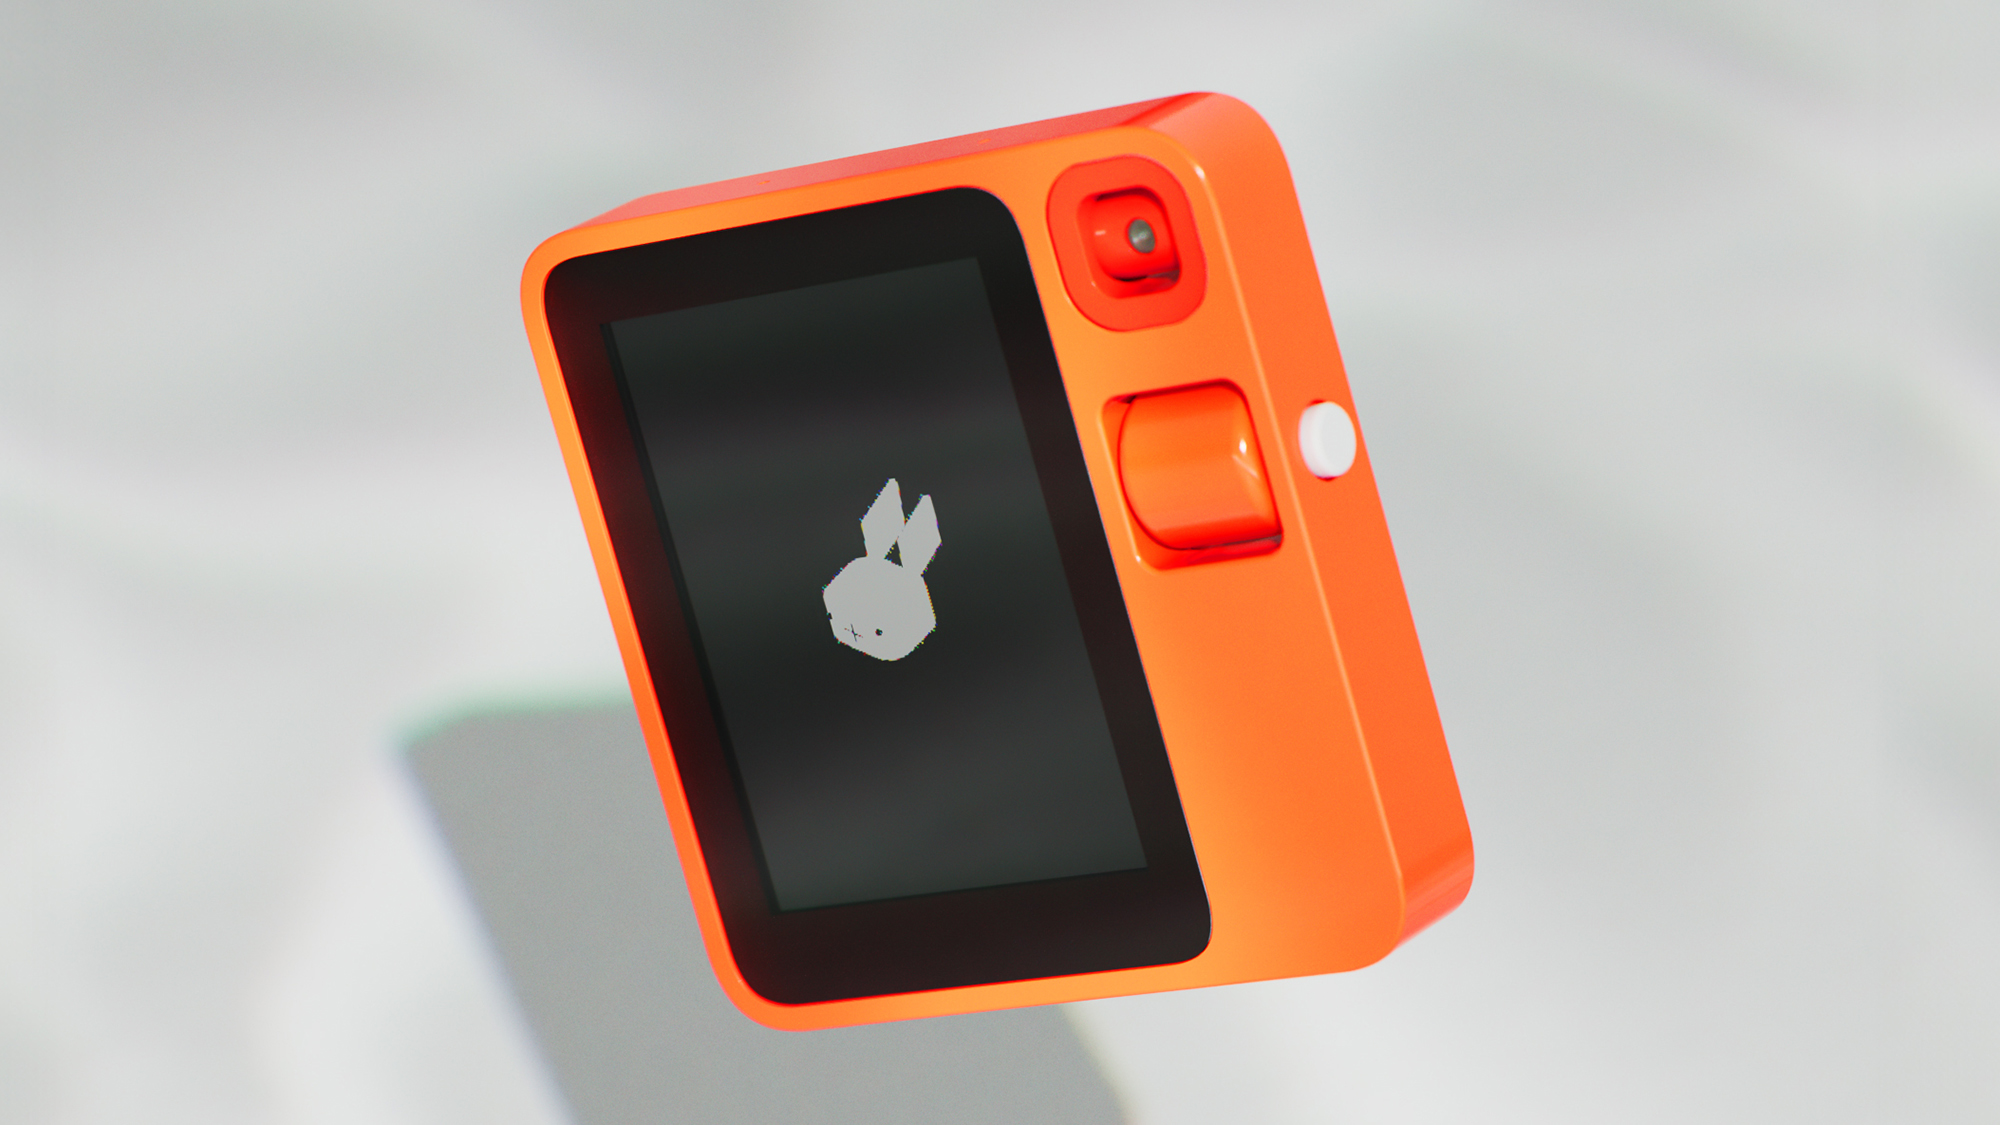
The Rabbit R1 has been found to contain multiple security vulnerabilities which not only could have allowed threat actors to read other people’s sensitive information, but also allowed them to send emails from the rabbit.tech subdomain.
Rabbitude, a community that formed around the unique AI assistant device, with the goal of reverse engineering the device, recently published two separate articles, outlining how in mid-May 2024, researchers gained access to the Rabbit codebase, where they found “several critical hardcoded API keys” in the code.