I’ve spent two and a half decades responding to cyber incidents or leading teams of people who do. Over that time, I’ve watched the threat landscape evolve from opportunistic attacks and early internet worms to organized cybercrime, ransomware syndicates, and nation-state campaigns. Each major shift brought new technology, new tactics, and new challenges for defenders.
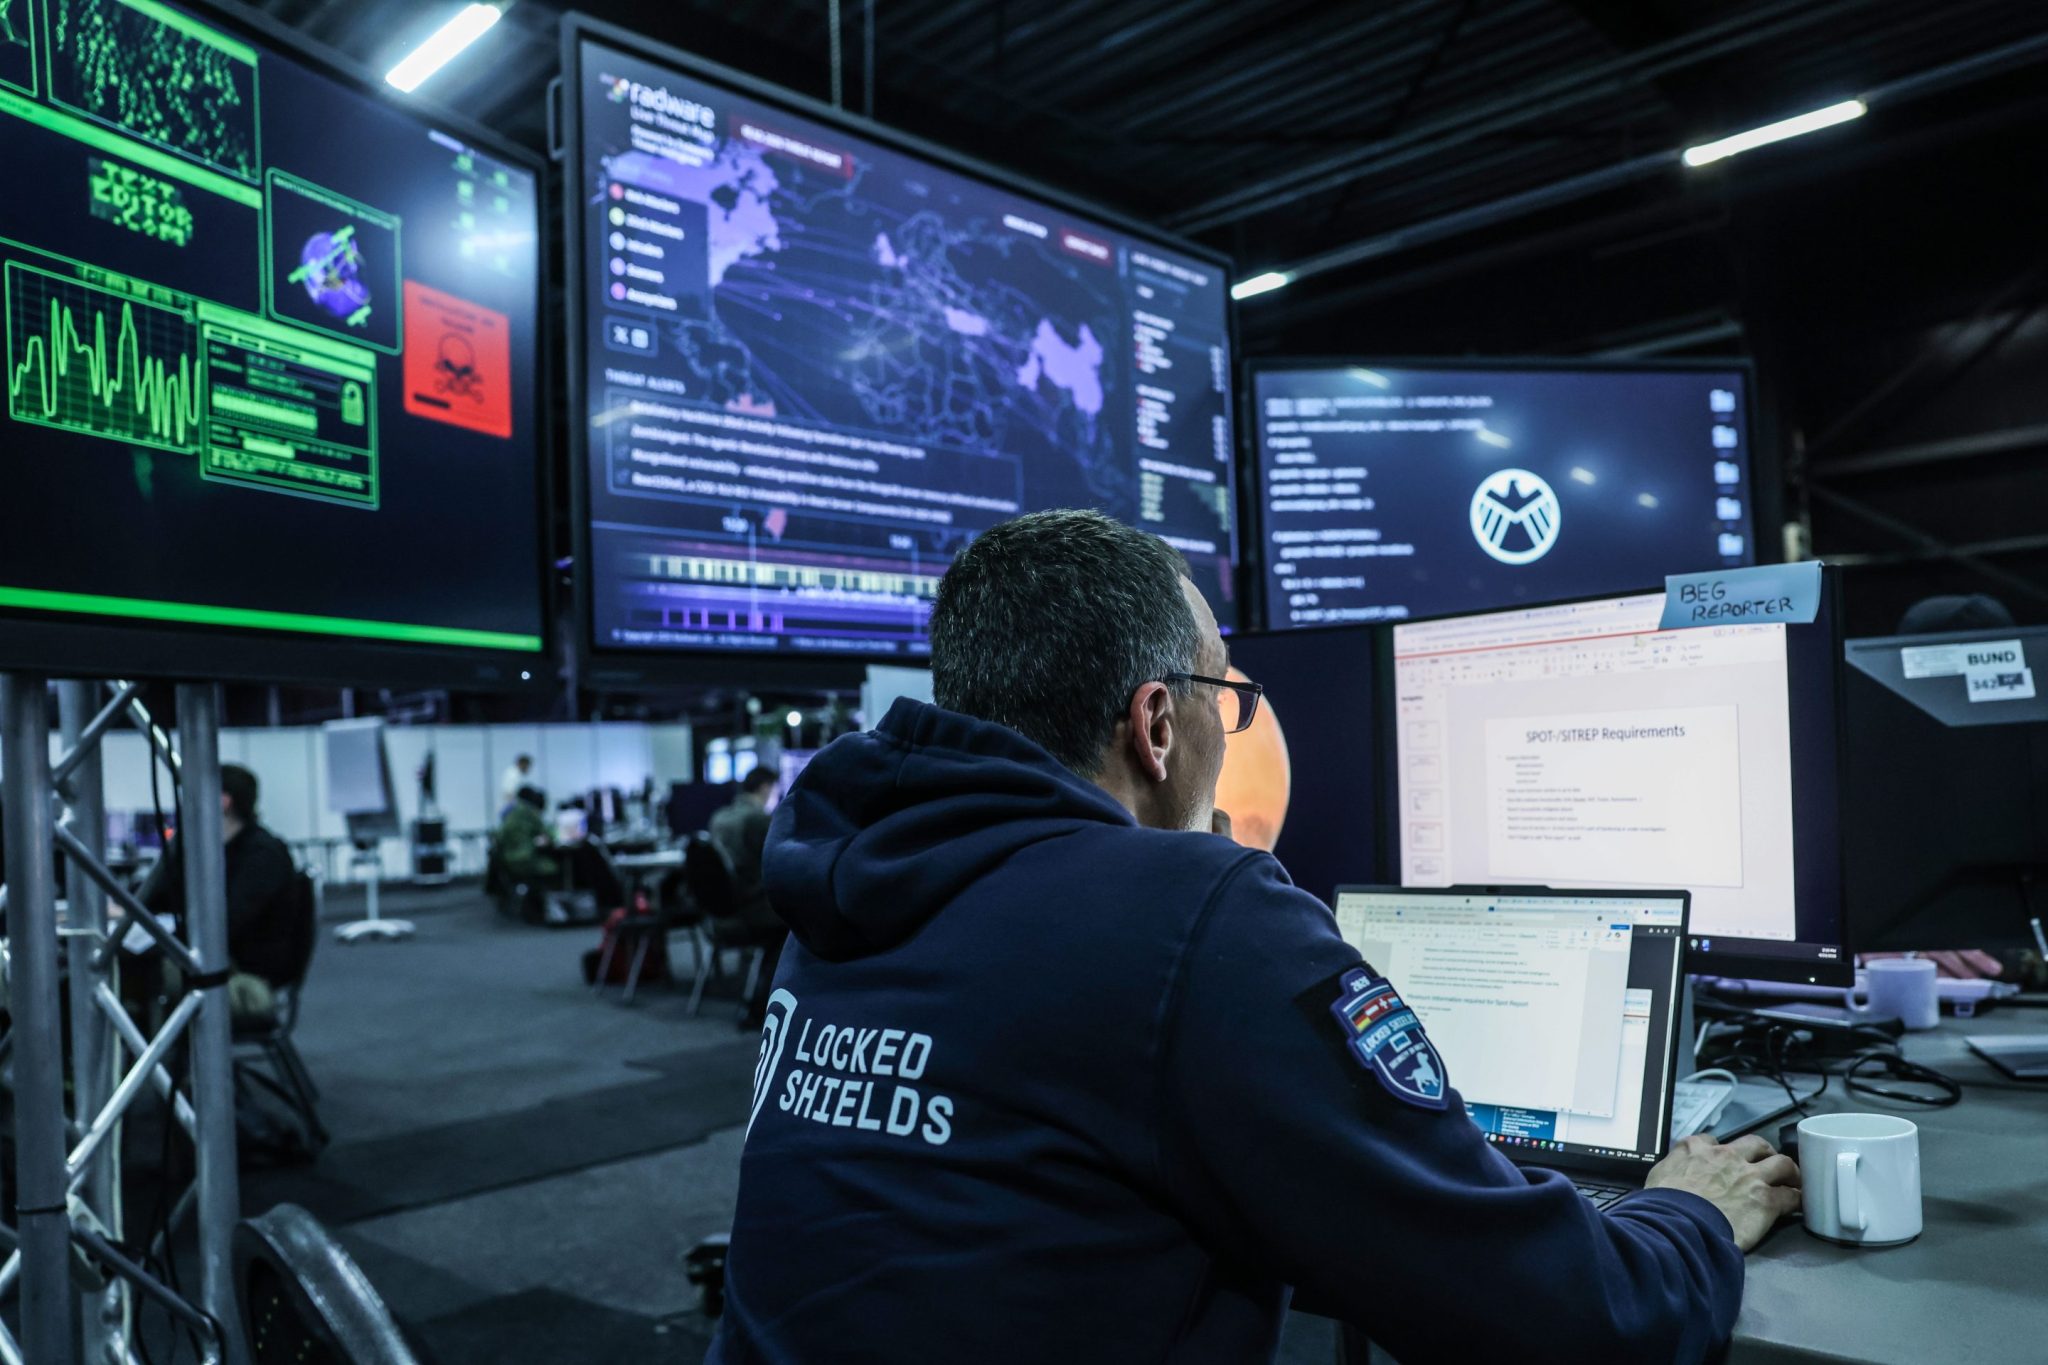
But one consistent part of the job is the people. The analysts who spent nights and weekends investigating suspicious activity, the incident responders making high-stakes decisions with incomplete information and working around the clock to restore critical systems.