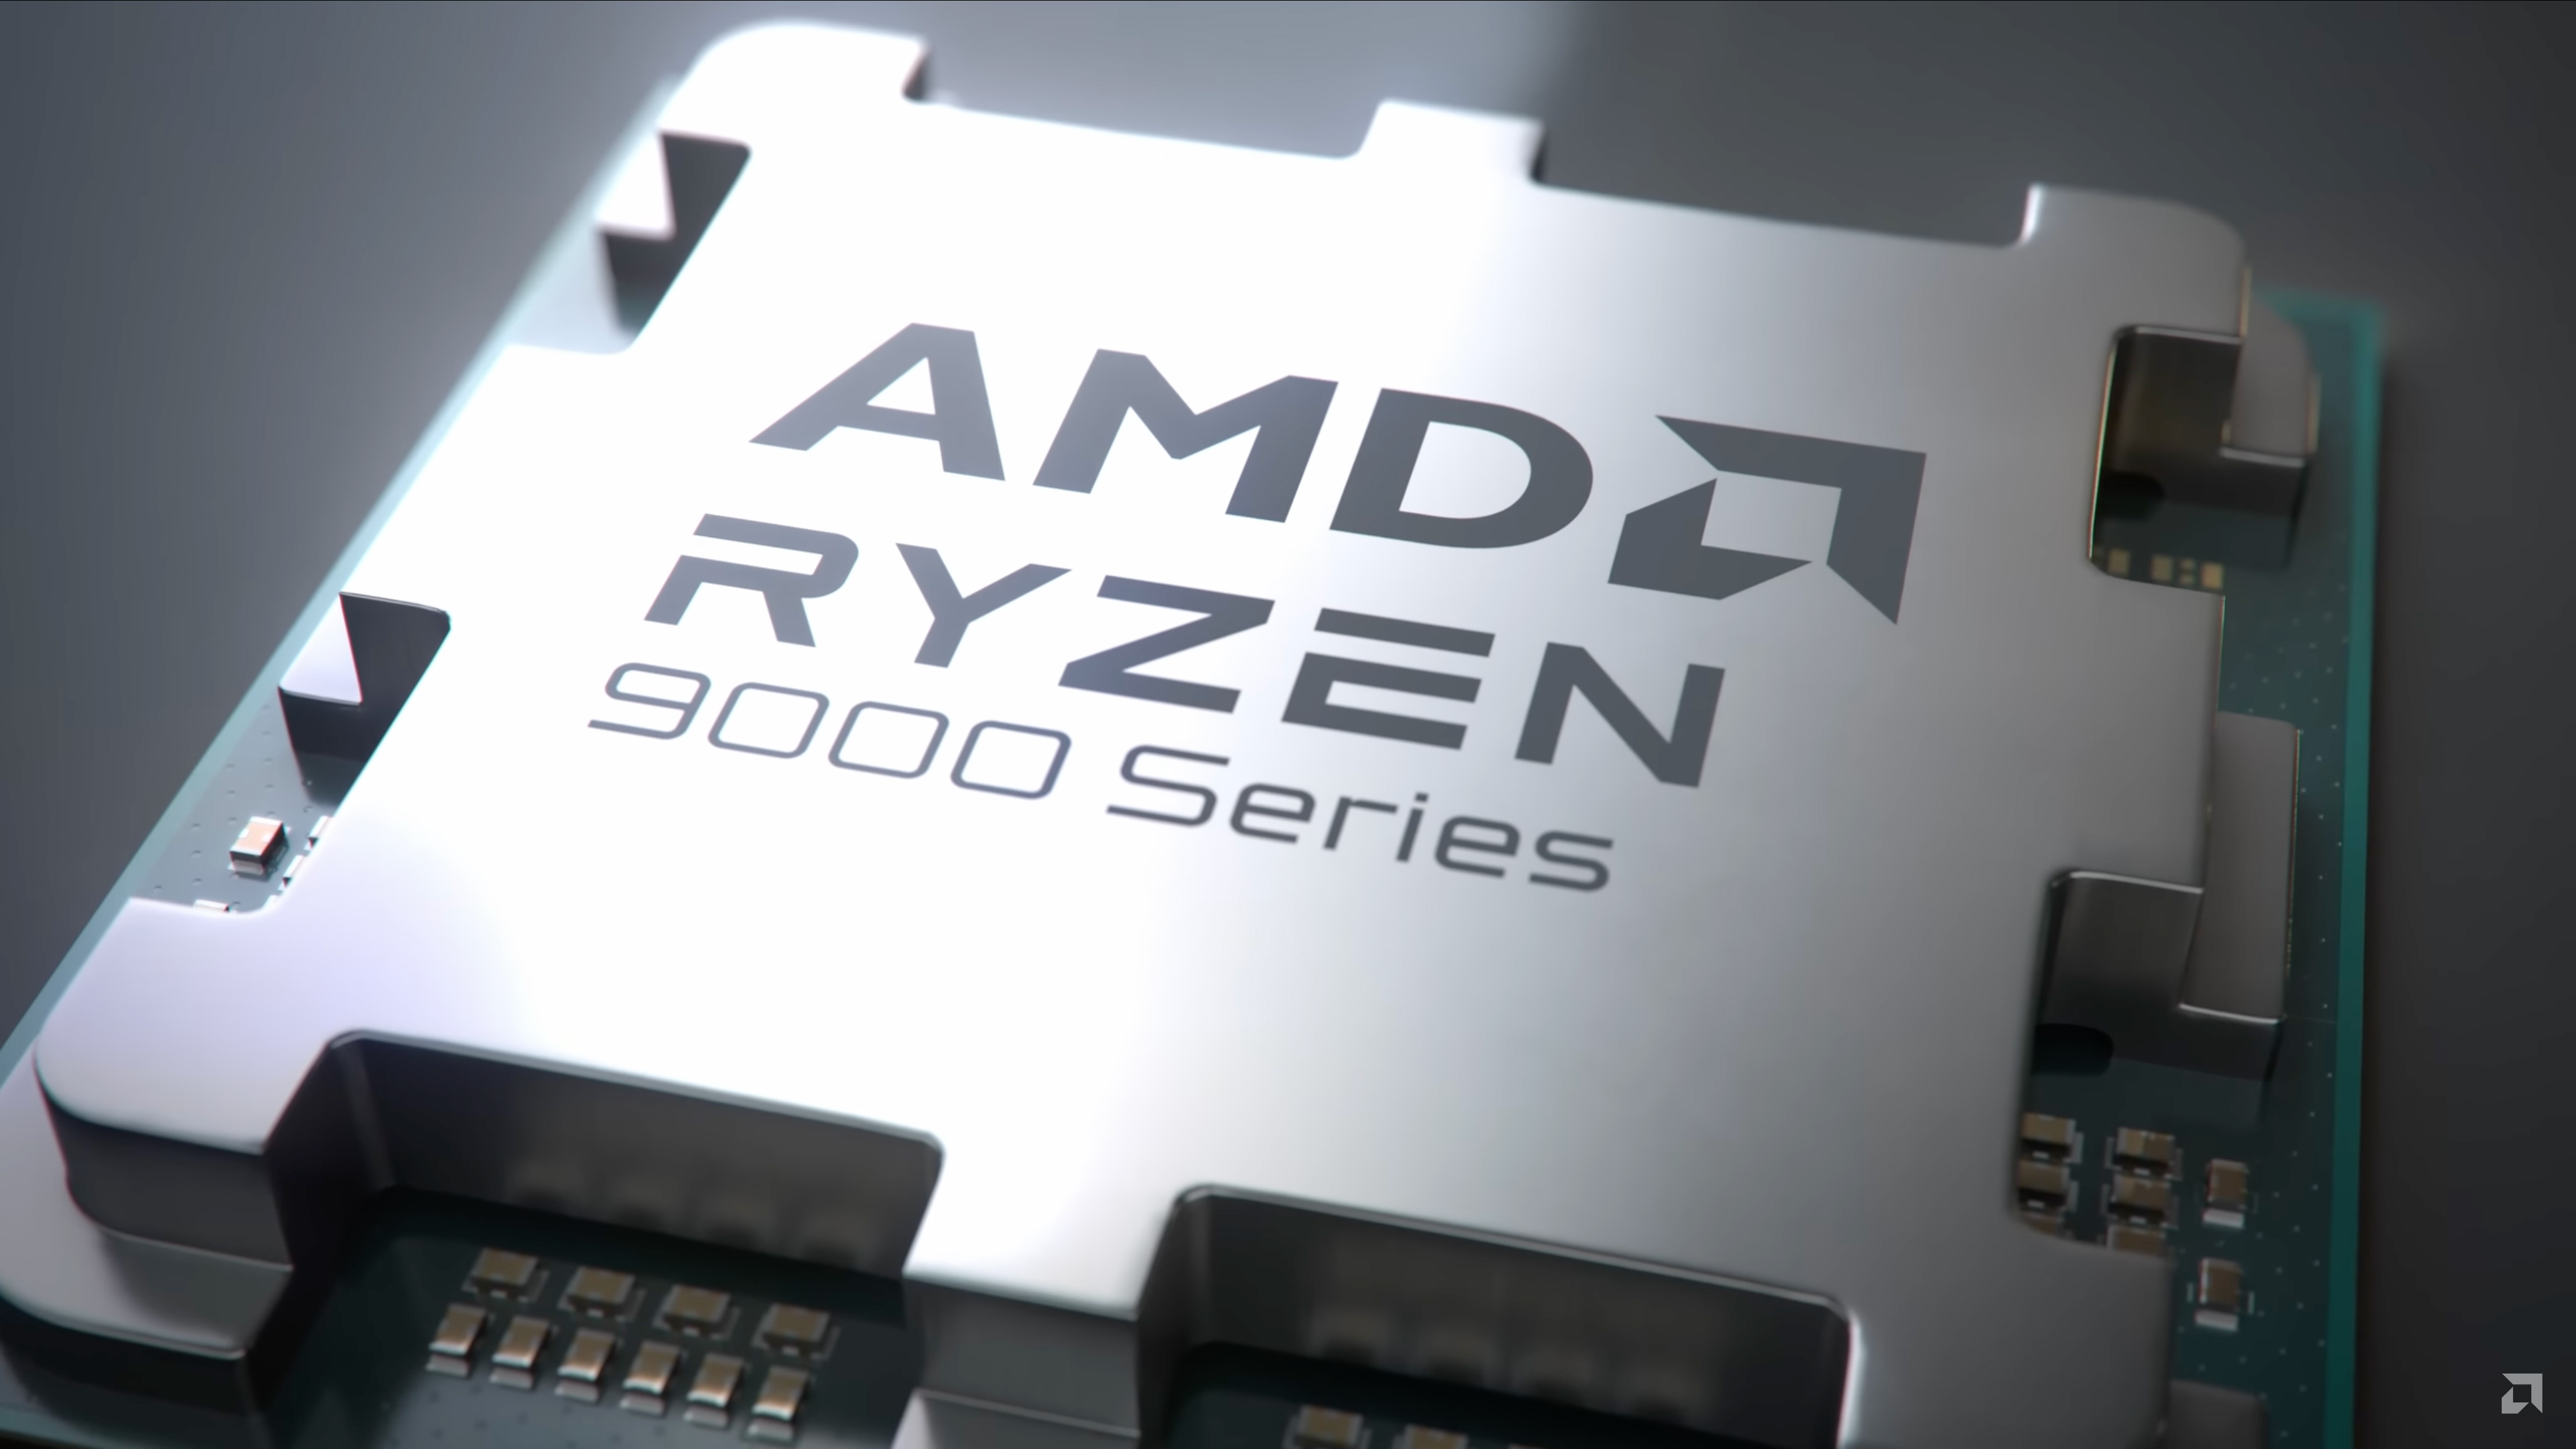
Last month, the Google Security Team identified a security vulnerability in AMD's CPUs ranging from Zen 1 to Zen 4 dubbed "EntrySign" that allowed malicious users with ring 0 access to load unsigned microcode patches. An update to the AMD security bulletin now adds Zen 5, in all its forms across server and mainstream product lines, to the list of impacted infrastructures.
The security flaw leverages an improper signature verification in AMD's microcode patch loader, allowing third parties to execute arbitrary microcode on your processor.