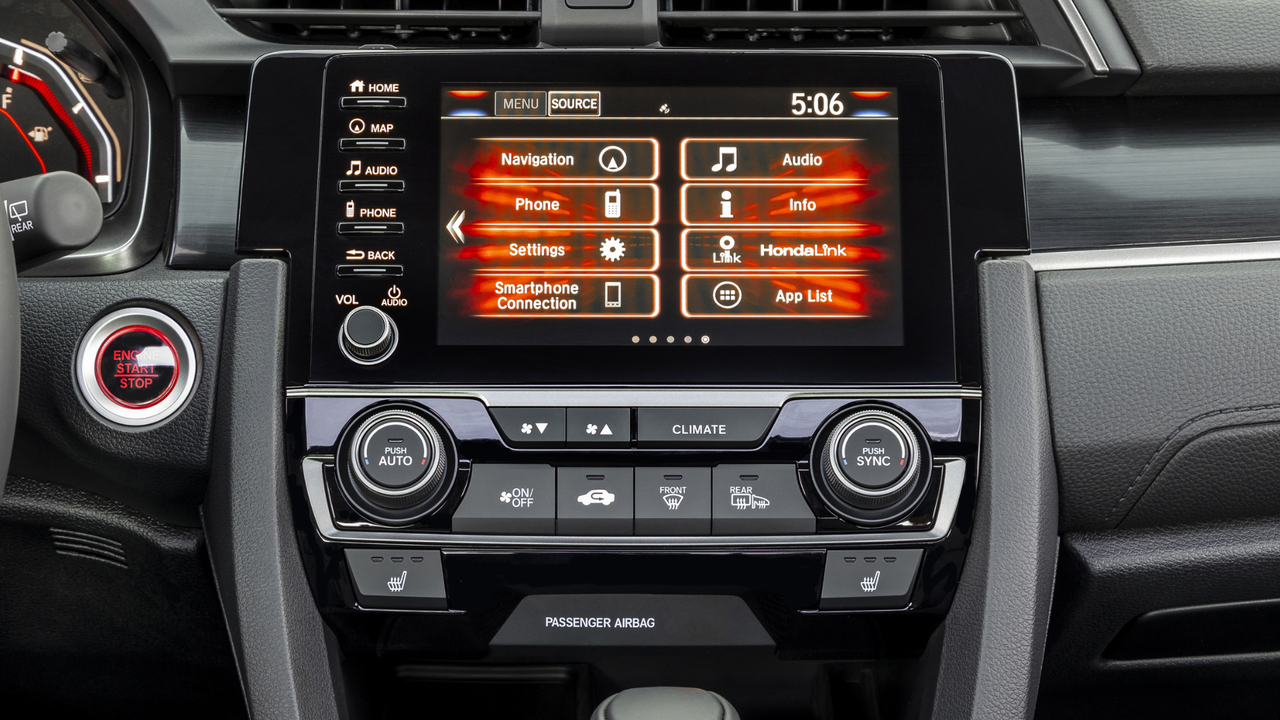
Software architect Eric McDonald discovered that the infotainment system of their 2021 Honda Civic has a glaring vulnerability through its front USB port. According to the post on their blog, Honda allows the head unit of this particular vehicle to be updated via USB. However, it apparently does not have strong security measures, with the hardware only looking for a signed AOSP (Android Open Source Project) file with a publicly known test key.
If you know how to set up a USB drive and sign it with this AOSP test key, you (or anyone else, for that matter) can potentially install anything on your head unit through the update path. While this is useful for tinkerers who want to get more out of their vehicles, McDonald also noted that it can be used for an “evil maid attack.” This method of compromising hardware uses the temporary physical access of a person (like a hotel maid, for example) to install malware on equipment. In their example, they said that a journalist could leave their car with a valet, and then the said valet could install malware on their infotainment system, thus giving the vulnerability the name “EvilValet.”