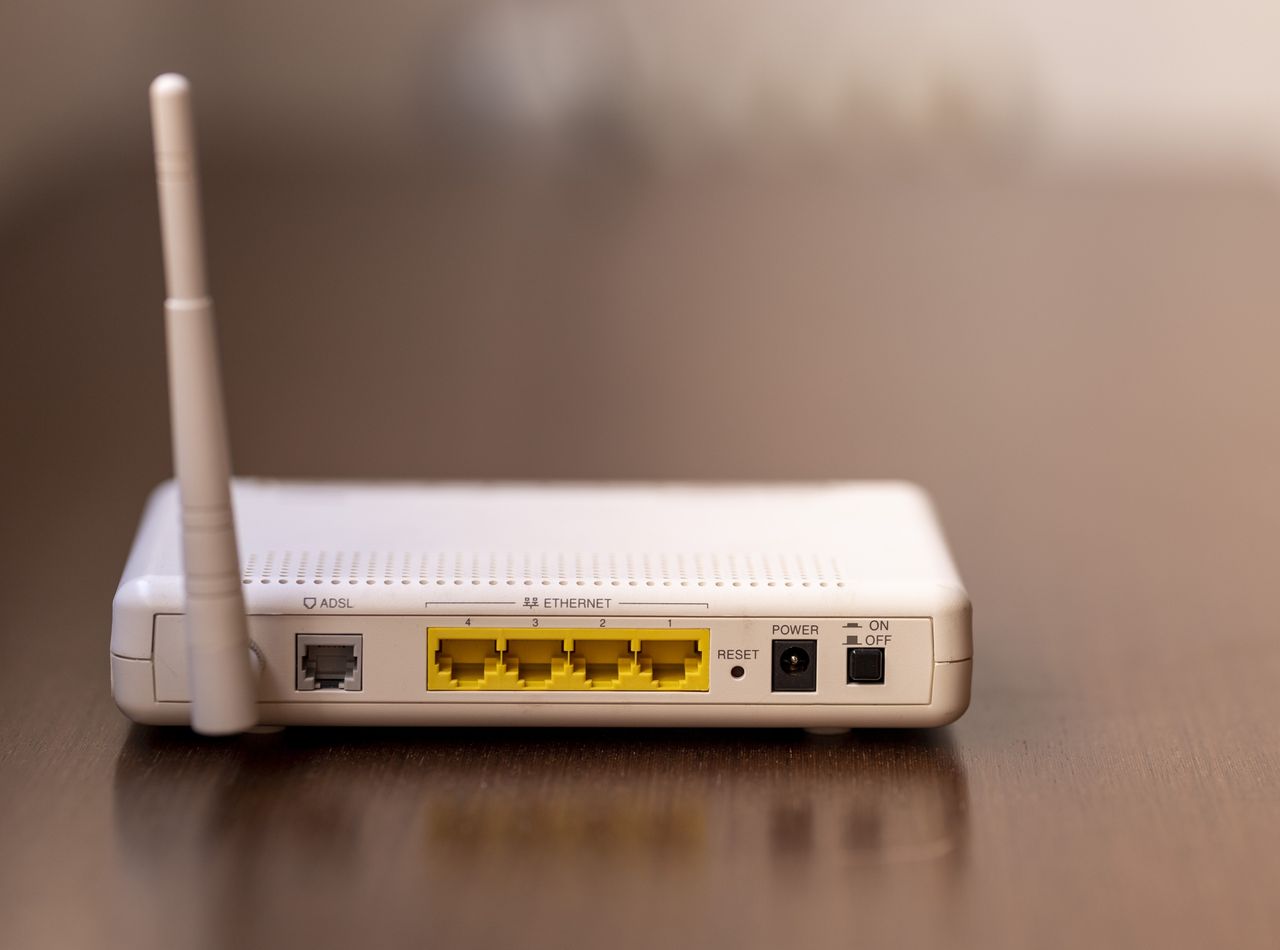
Security researchers have found three different backdoor-like implants hidden in firmware for routers manufactured by Shenzhen Zhibotong Electronics, better known as ZBT. The hardware is sold around the world under a bewildering array of brands, meaning you may not even realize you're using a ZBT router. The research, published by security firm VulnCheck, began with a Zbtlink AX3000 router. Researchers found that its firmware contained an implant that they dubbed ENDLESSDOORS, as it automatically phones home to a command-and-control server and can execute arbitrary commands as root.
ENDLESSDOORS is essentially a remote-control system embedded directly into the router's firmware. It starts automatically at boot and disguises itself as a normal Linux kernel process called kworker. The router periodically connects to a hard-coded server and announces itself. There's no meaningful authentication or encryption involved. Commands received from the server are passed directly to a shell running as root, and the implant can also establish an interactive root shell.