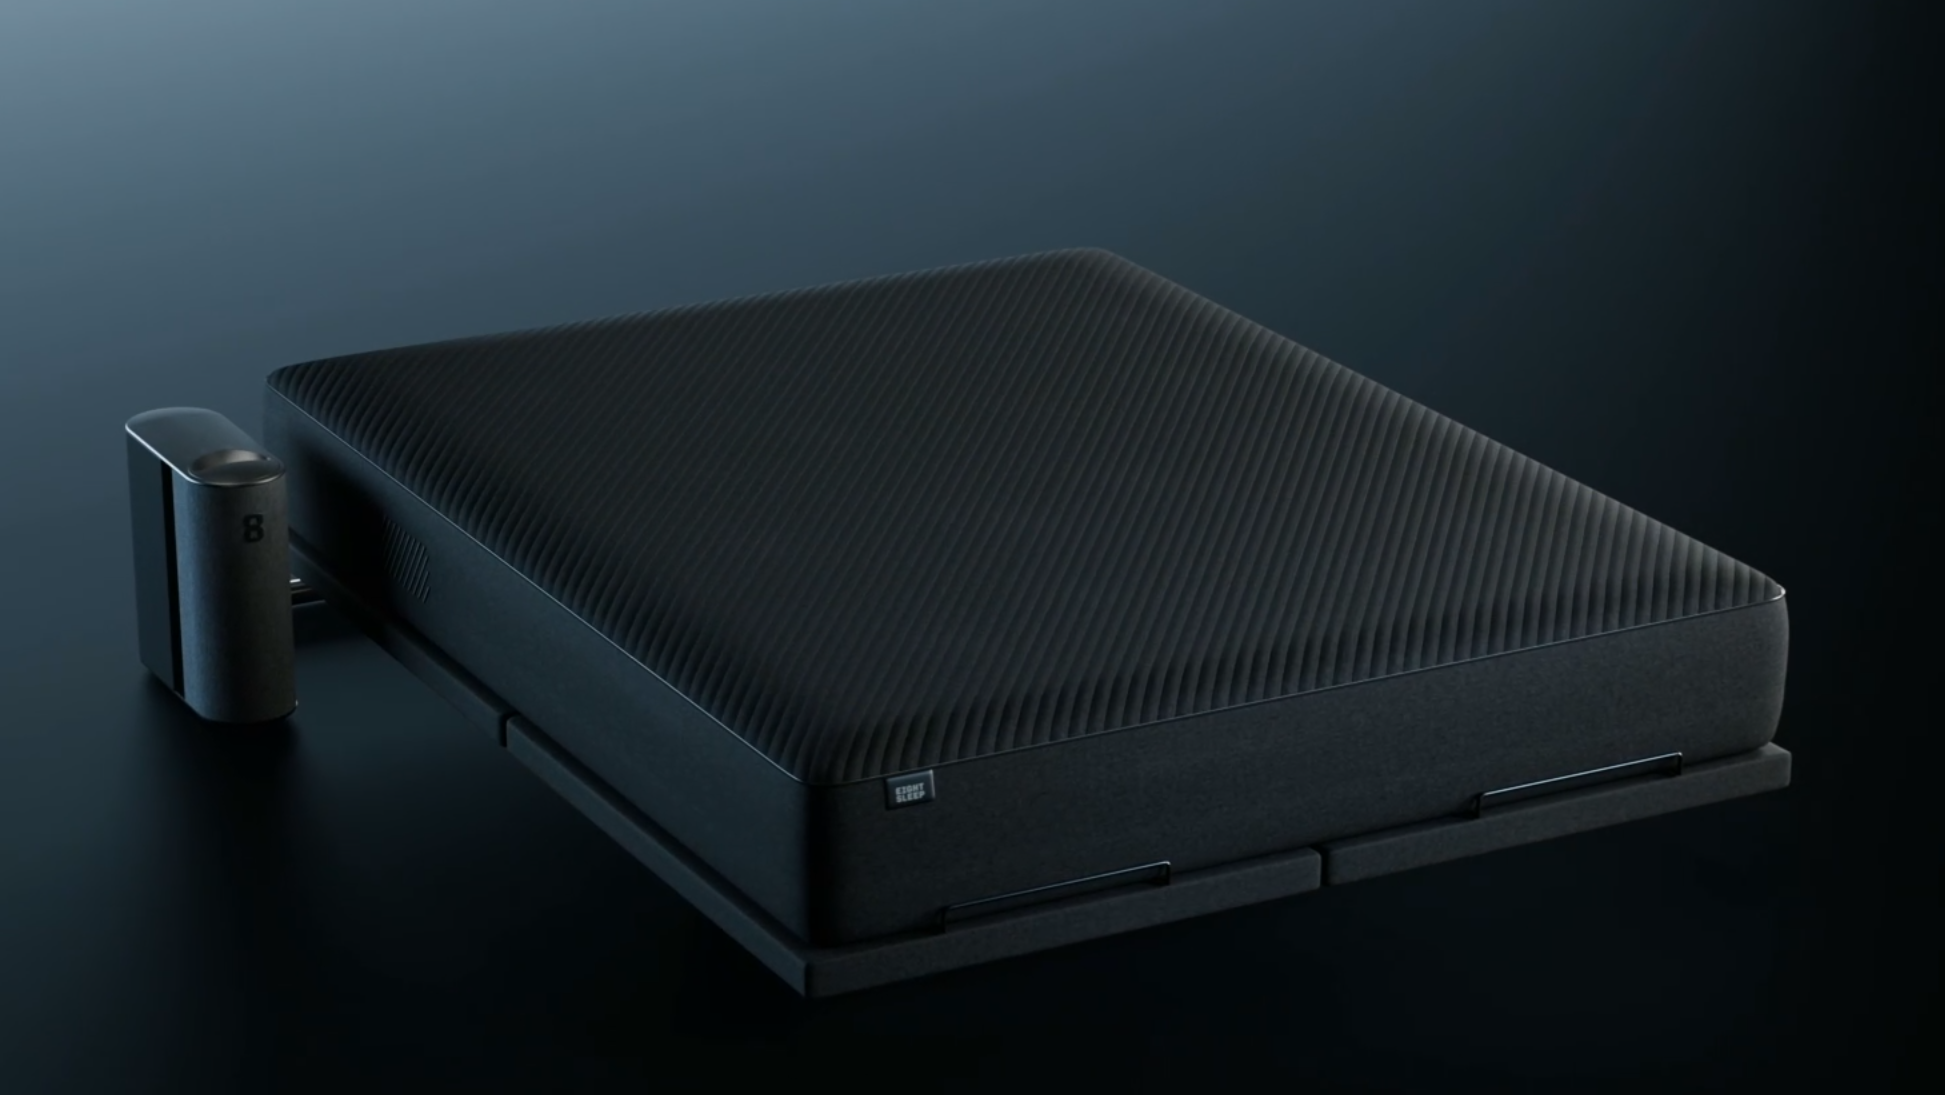
Cybersecurity researcher Dylan Ayrey of Truffle Security has shared a detailed blog post highlighting his experience with Eight Sleep smart beds since his discovery of an exposed AWS key inside of its firmware, prompting him to deeply investigate its security issues and find ways to alleviate them. Besides the AWS key problem, he also discovered a backdoor allowing SSH (Secure Shell) backdoor access and full arbitrary code execution capabilities, making Eight Sleep beds a disastrously unsafe device to keep on a home network for not just bed surveillance concerns, but the security of all devices involved.
Back in December, Ayrey made a Tweet from his @InsecureNature account encouraging his followers to guess what appliance of his had the major AWS key security issue, and this was before he even started talking about the SSH backdoor allowing arbitrary code execution on the bed.