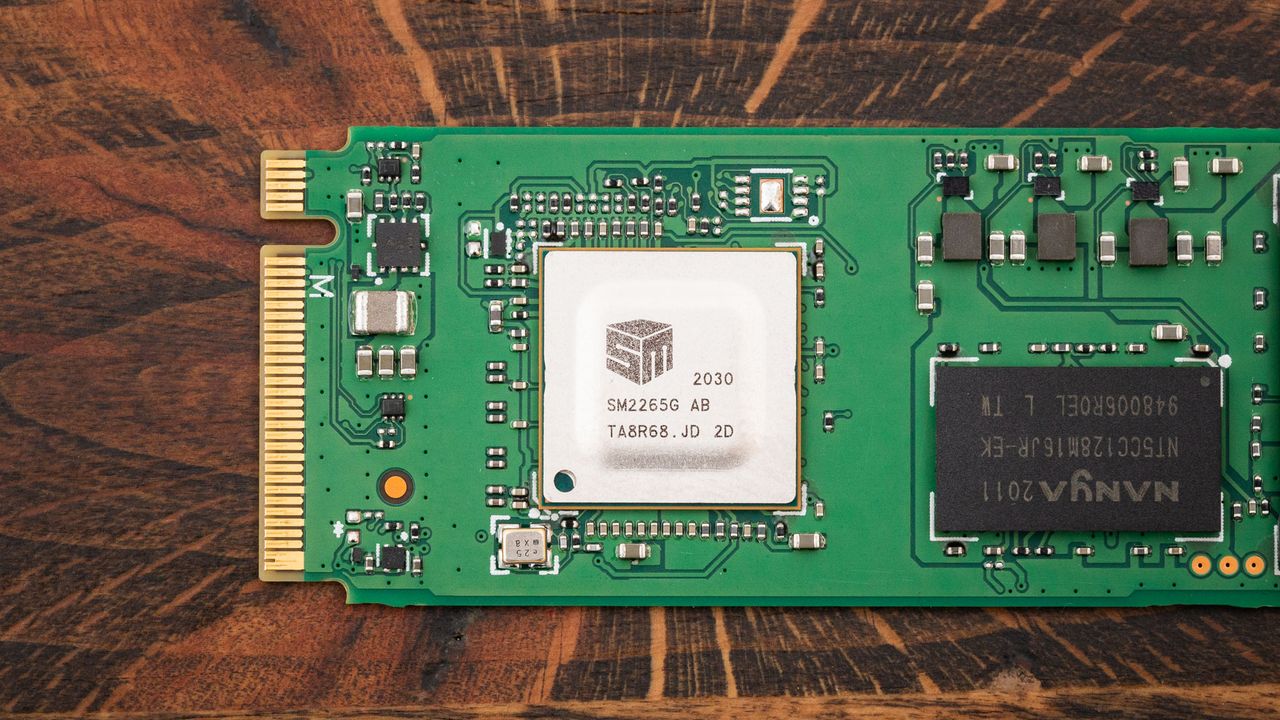
Security researchers at Graz University of Technology in Austria have published a paper describing a side-channel attack that lets a malicious website identify what other sites and apps a visitor has open by measuring SSD access latency through JavaScript inside a standard browser sandbox. The technique, called FROST (Fingerprinting Remotely using OPFS-based SSD Timing), correctly identified visited websites with roughly 89% accuracy and running applications with roughly 96% accuracy on a test Mac, requires nothing from the victim beyond visiting the attacker's page, and works across different browsers.
FROST exploits the Origin Private File System (OPFS), a browser API that lets websites create and store files on a user's local disk without prompting for permission. Previous SSD side-channel attacks that we’ve seen require native code running through privileged kernel interfaces, but FROST eliminates that requirement.