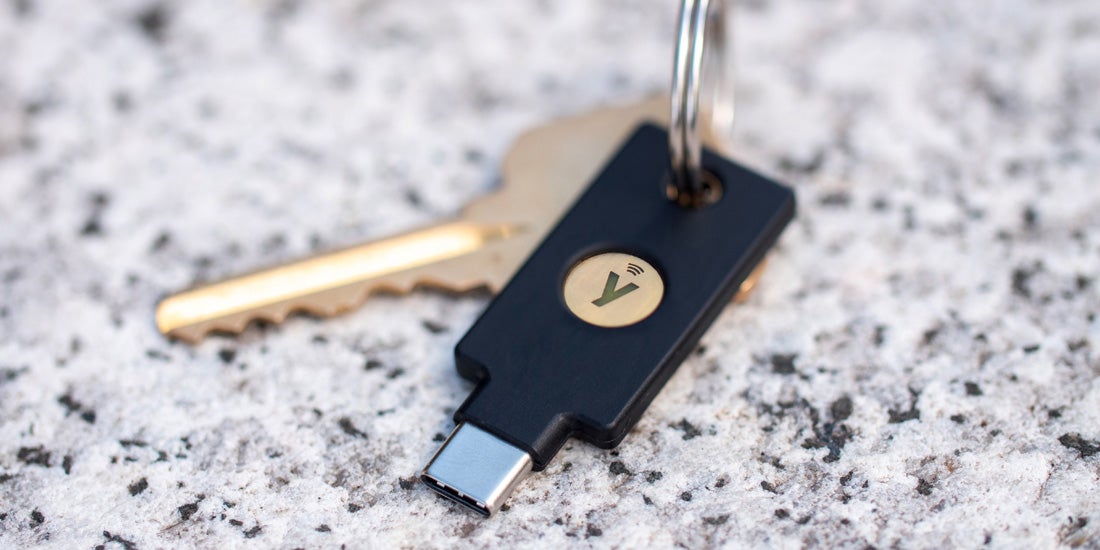
A critical security vulnerability has been discovered affecting many YubiKey two-factor authentication devices, breaking their security with no patch in sight. Yubico's security advisory confirmed that Yubikey 5 and Security Key Series prior to firmware 5.7 are forever vulnerable to a high-level cloning attack. However, the average user should not worry too much about the vulnerability.
Yubikey 5 series, YubiHSM 2, and other two-factor authentication products by Yubico and other vendors utilizing the Infineon SLB96xx series TPM chip are vulnerable to the newly found attack. Security researchers at NinjaLab tested Yubikey 5 products — due to them being the most common FIDO authenticator tools — and found that an issue in Infineon's library allows bad actors to clone the keys. All Infineon chips, going back 14 years, which run any version of its cryptographic library, are vulnerable to the same attack.