- SMS sign-in links rely on possession alone, leaving private accounts dangerously exposed
- Weak tokens allow attackers to guess valid links and access other users ' accounts
- Unencrypted text messages remain a fragile foundation for account authentication
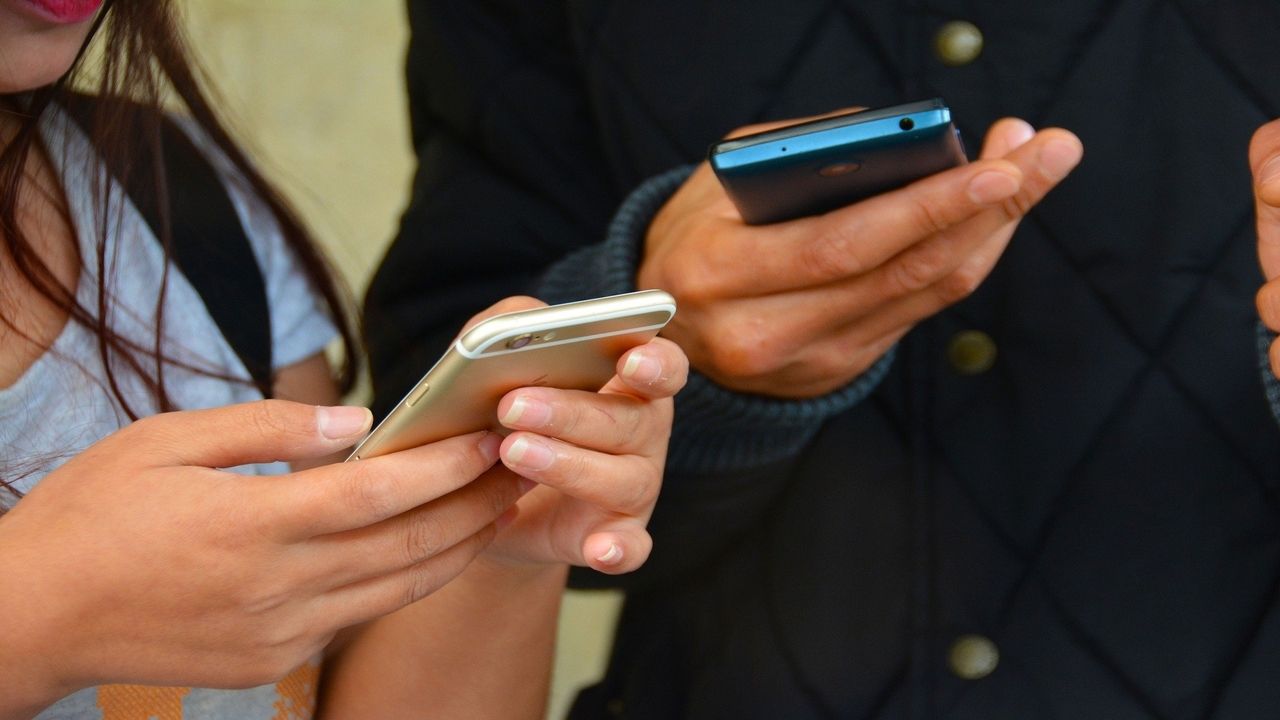
Many online services now rely on sign-in links or codes delivered through text messages instead of traditional passwords, which reduces steps during account access and avoids storing password databases, which attackers often breach.