Get all your news in one place.
100's of premium titles.
One app.
Start reading
Windows Central
Windows Central
Technology
Kevin Okemwa

Microsoft issues mitigation for critical Windows 11 BitLocker flaw exploited with a USB key — "Can't come up with an explanation beside the fact that this was intentional."

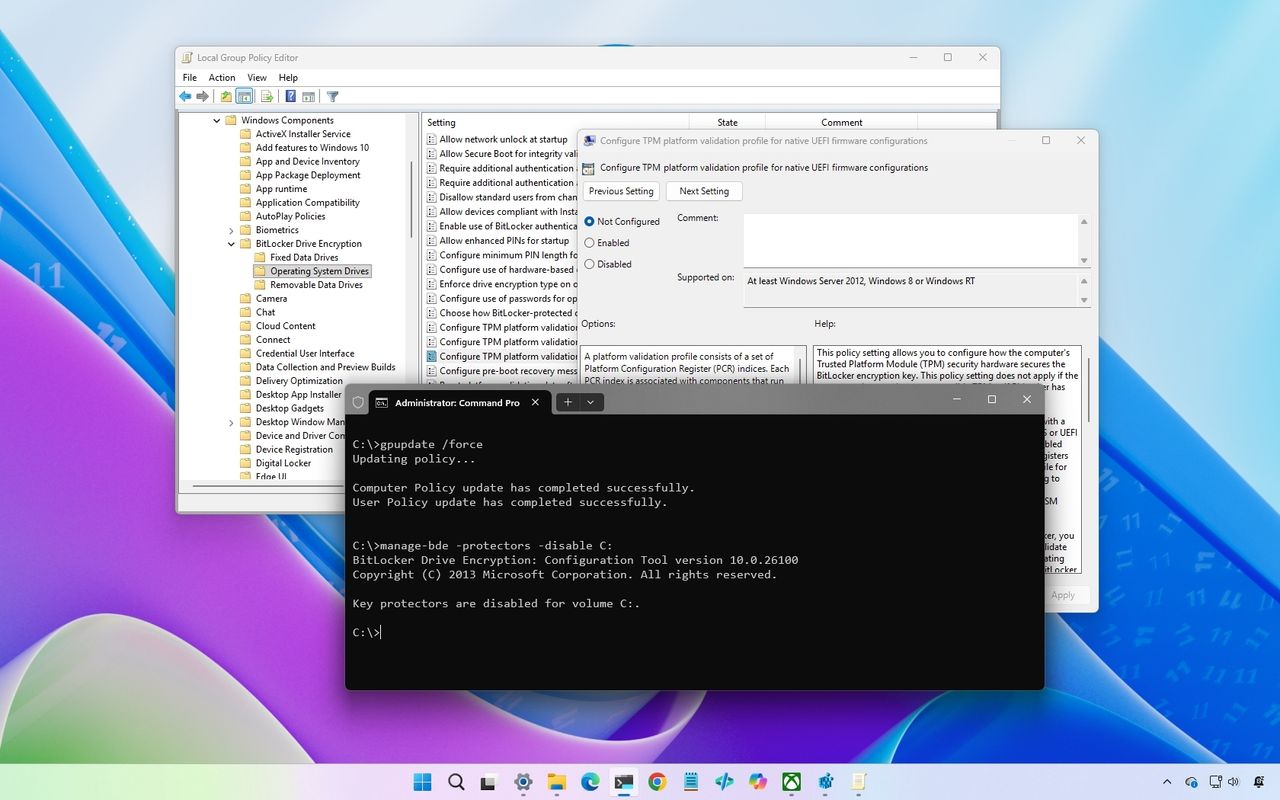
Windows 11 desktop showing group policy editor and command prompt. The editor highlights a setting, while command prompt displays a successful encryption command.

"Just can't come up with an explanation beside the fact that this was intentional. Also for whatever reason, only windows 11 (+Server 2022/2025) are affect, windows 10 is not," explained security researcher Chaotic Eclipse (better known as Nightmare-Eclipse) after they managed to bypass Windows 11's sophisticated BitLocker security feature using a USB stick.

The security sleuth posted the zero-day exploit known as YellowKey, which essentially enabled them to access a locked file. As explained by our friends over at Tom's Hardware:

Sign up to read this article
Read news from 100's of titles, curated specifically for you.
Already a member? Sign in here
Related Stories
Top stories on inkl right now
One subscription that gives you access to news from hundreds of sites
Already a member? Sign in here
Our Picks
Fourteen days free
Download the app
One app. One membership.
100+ trusted global sources.