Get all your news in one place.
100's of premium titles.
One app.
Start reading
Windows Central
Windows Central
Technology
Kevin Okemwa

Microsoft Copilot's own default configuration exposed users to the first-ever "zero-click" AI attack, but there was no data breach

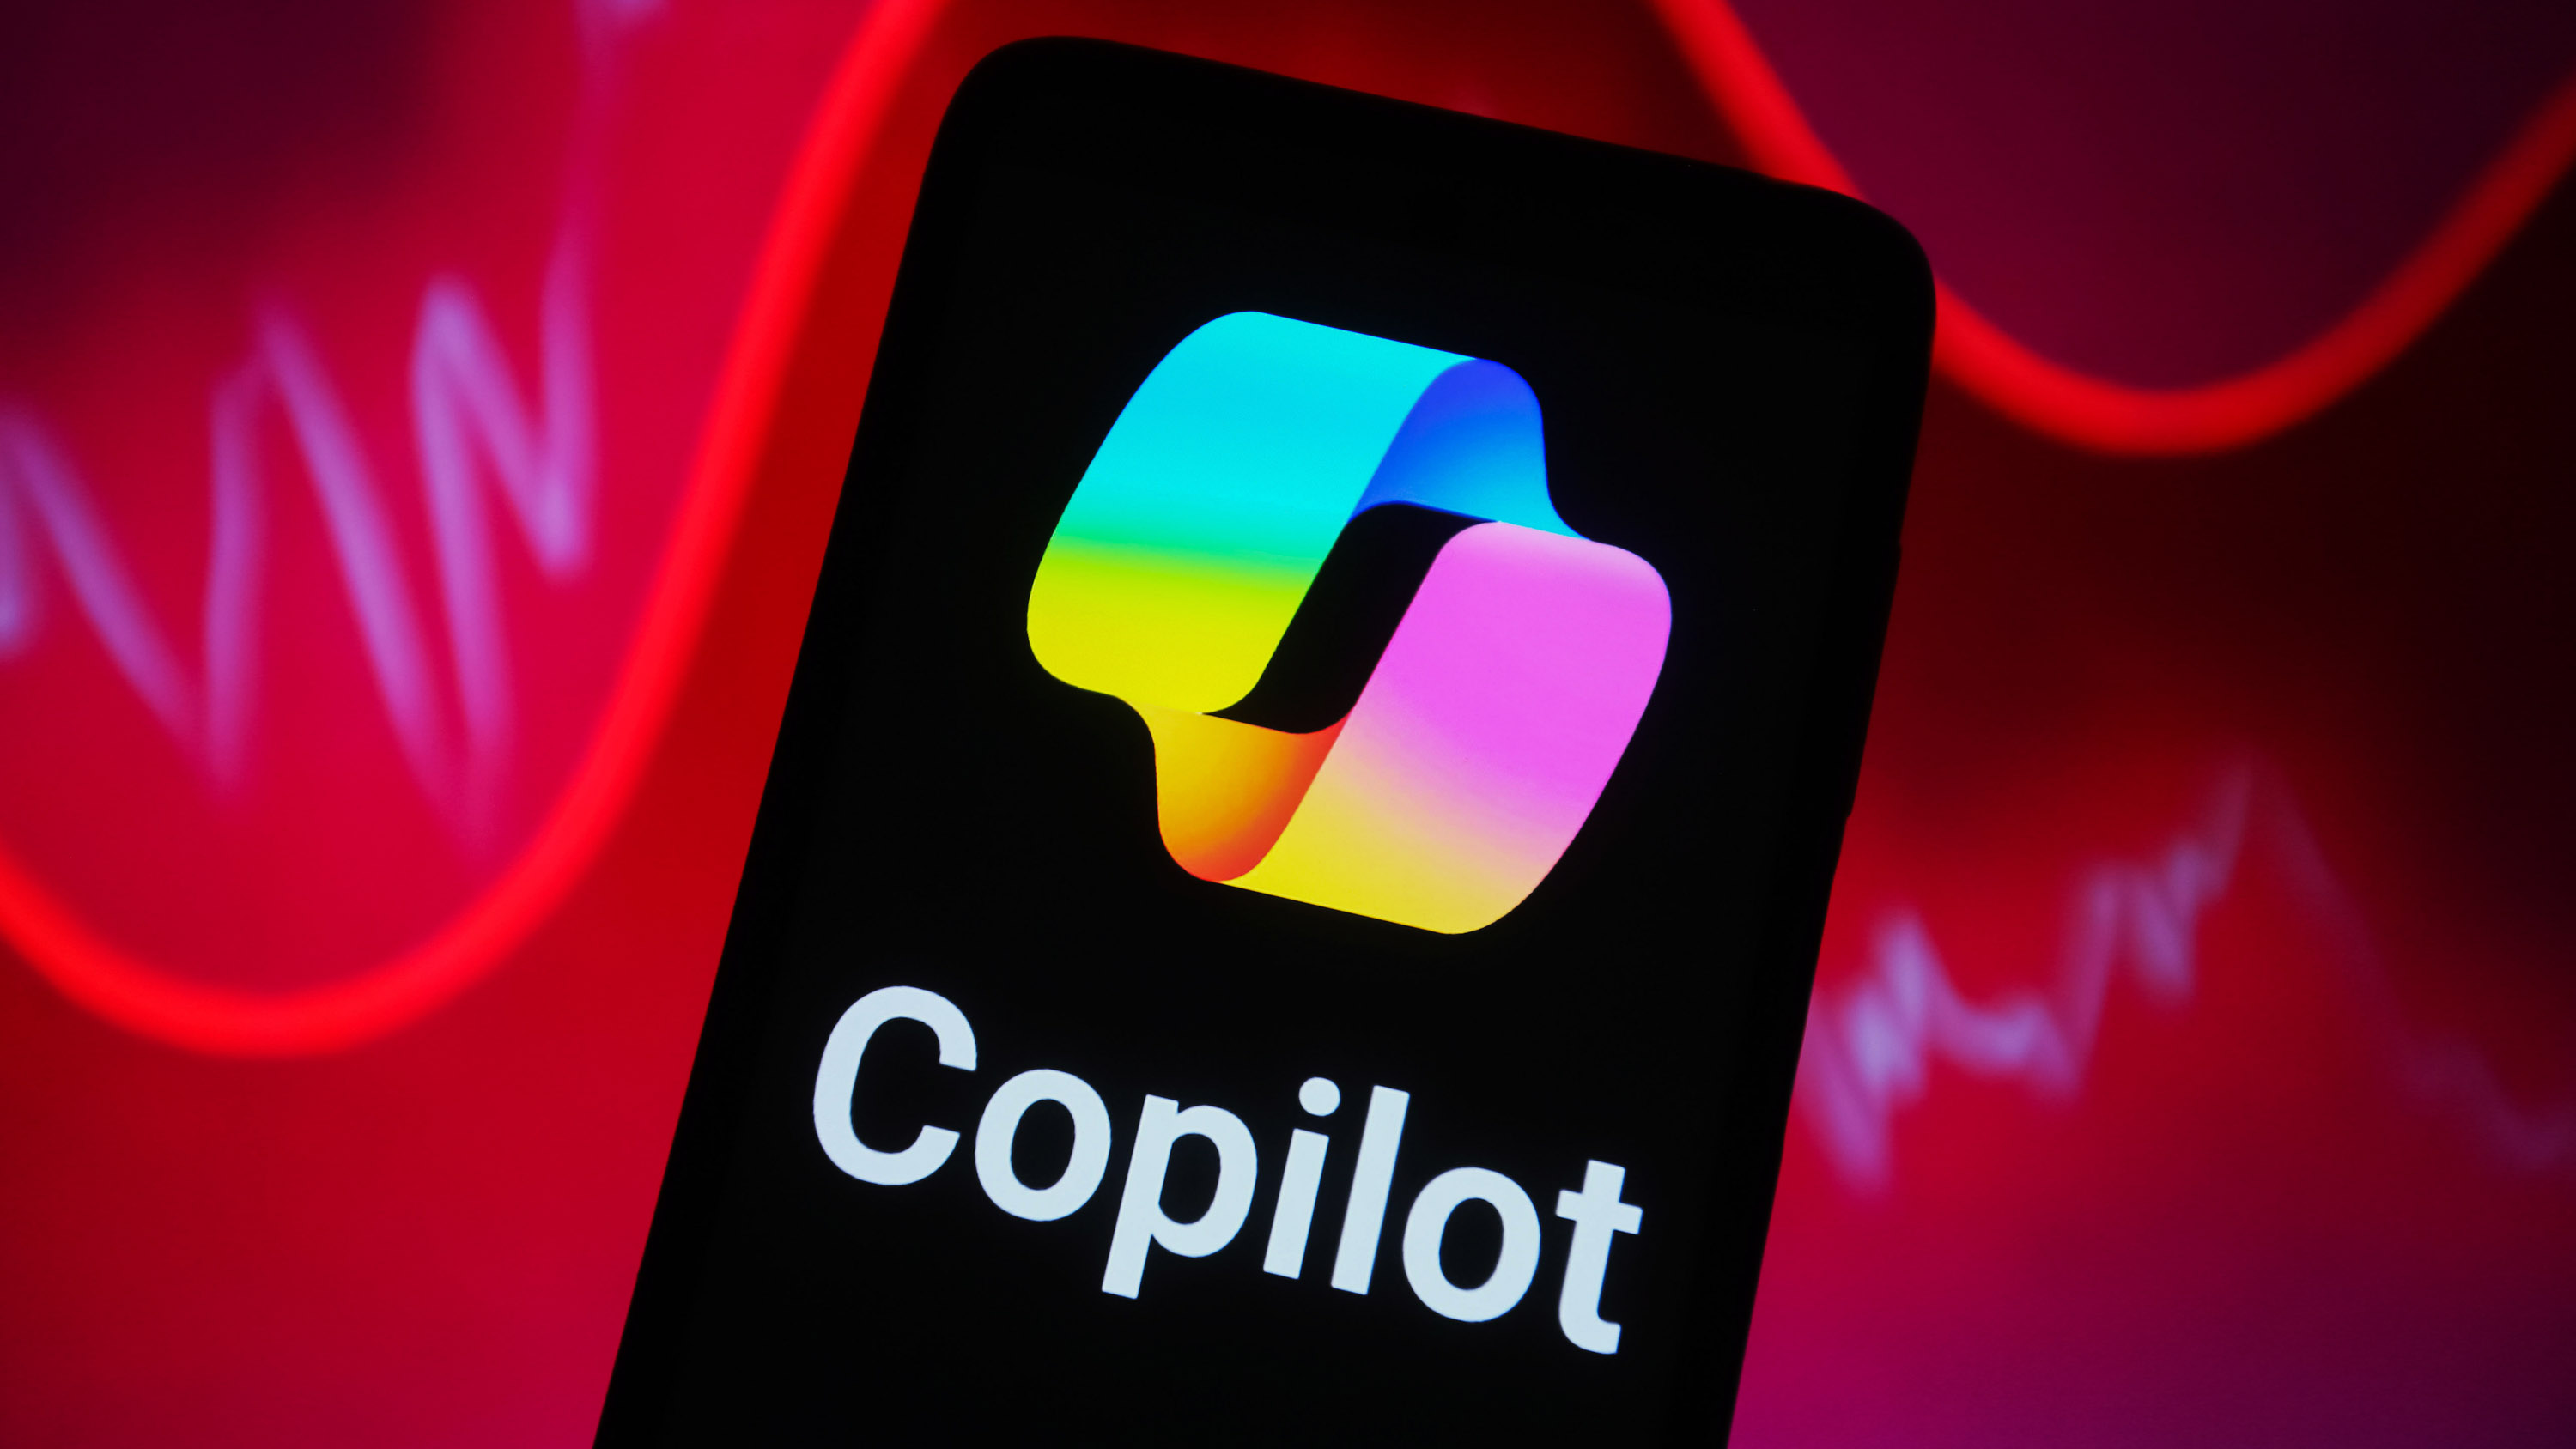
In this photo illustration, Microsoft Copilot AI logo is seen on a smartphone screen.

Security researchers from Aim Labs uncovered a critical attack dubbed 'EchoLeak' impacting Microsoft 365 Copilot. The vulnerability could potentially allow bad actors to gain unauthorized access to sensitive data from Microsoft 365 Copilot users without any interaction.

The security researchers presented their findings to Microsoft, prompting the tech giant to assign the vulnerability the identifier CVE-2025-32711. EchoLeak marks the first known zero-click attack on an AI agent (via Fortune).
Sign up to read this article
Read news from 100's of titles, curated specifically for you.
Already a member? Sign in here
Related Stories
Top stories on inkl right now
One subscription that gives you access to news from hundreds of sites
Already a member? Sign in here
Our Picks
Fourteen days free
Download the app
One app. One membership.
100+ trusted global sources.