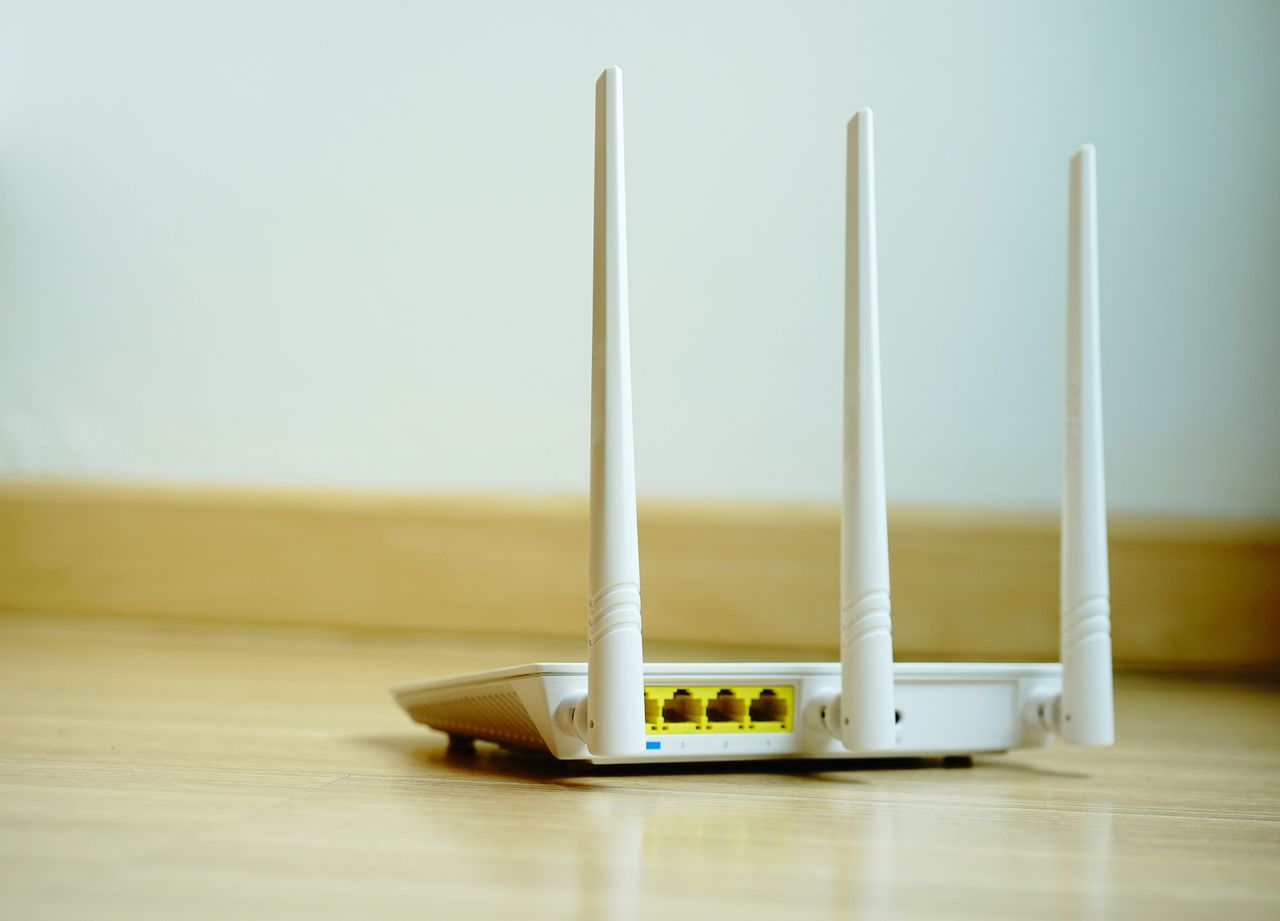
The CERT Coordination Center (CERT/CC), a U.S. government-backed cybersecurity group at Carnegie Mellon University's Software Engineering Institute, disclosed a firmware flaw on July 6 that can hand attackers full administrative control over several Tenda networking devices. The vulnerability, tracked as CVE-2026-11405, is an undocumented authentication backdoor in the affected models' firmware that bypasses the normal login process and grants access to the devices' web management interface without valid credentials. Compounding the risk, there is currently no security patch available, as Tenda — a Shenzhen-based budget networking brand with a large presence in India and other markets — is yet to respond despite CERT/CC reaching out on the issue.
CERT/CC lists five affected firmware versions spanning the FH1201, W15E, AC10, AC5, and AC6 router families. The advisory, which credits an anonymous researcher for the finding, does not describe this list as exhaustive. The list covers only the specific builds the researcher reported to CERT/CC, as there is no vendor-confirmed scope. According to the advisory, the flaw resides inside the routers' built-in web server, where an undocumented authentication routine allows administrative access without requiring the configured administrator credentials.