Get all your news in one place.
100's of premium titles.
One app.
Start reading
PC Gamer
PC Gamer
Jeremy Laird

Hard to believe but Secure Boot BIOS security has been compromised on hundreds of PC models from big brands because firmware engineers used four-letter passwords

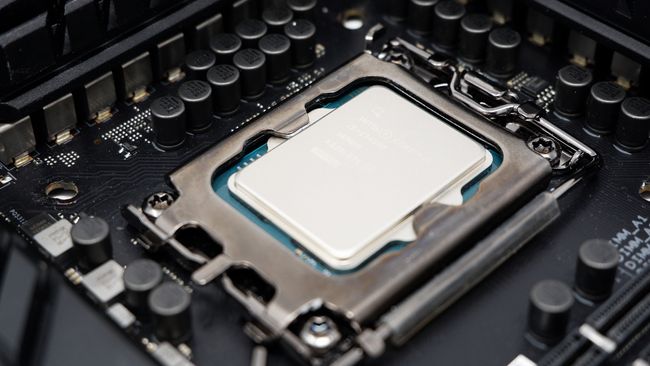
PC detail.

Now, I'll admit my own password hygiene isn't always the best, though I have graduated from the days when I used "xxxxxx" for a few non-critical accounts under the reverse psychology assumption that it's so obviously insecure, nobody would bother trying it. Genius, I know. But even I realise a four-character password is a big no-no.

And yet that's exactly what was used to protect an encrypted file that was critical to the fundamental integrity of the Secure Boot, a UEFI BIOS security layer designed to ensure that a device boots using only the software that is trusted by the PC maker itself.
Sign up to read this article
Read news from 100's of titles, curated specifically for you.
Already a member? Sign in here
Related Stories
Top stories on inkl right now
One subscription that gives you access to news from hundreds of sites
Already a member? Sign in here
Our Picks
Fourteen days free
Download the app
One app. One membership.
100+ trusted global sources.