- Older versions of Post SMTP allowed hackers to read all emails
- They could also reset the admin password and read the notification email, gaining access to the account
- More than 160,000 WordPress sites are running the vulnerable version
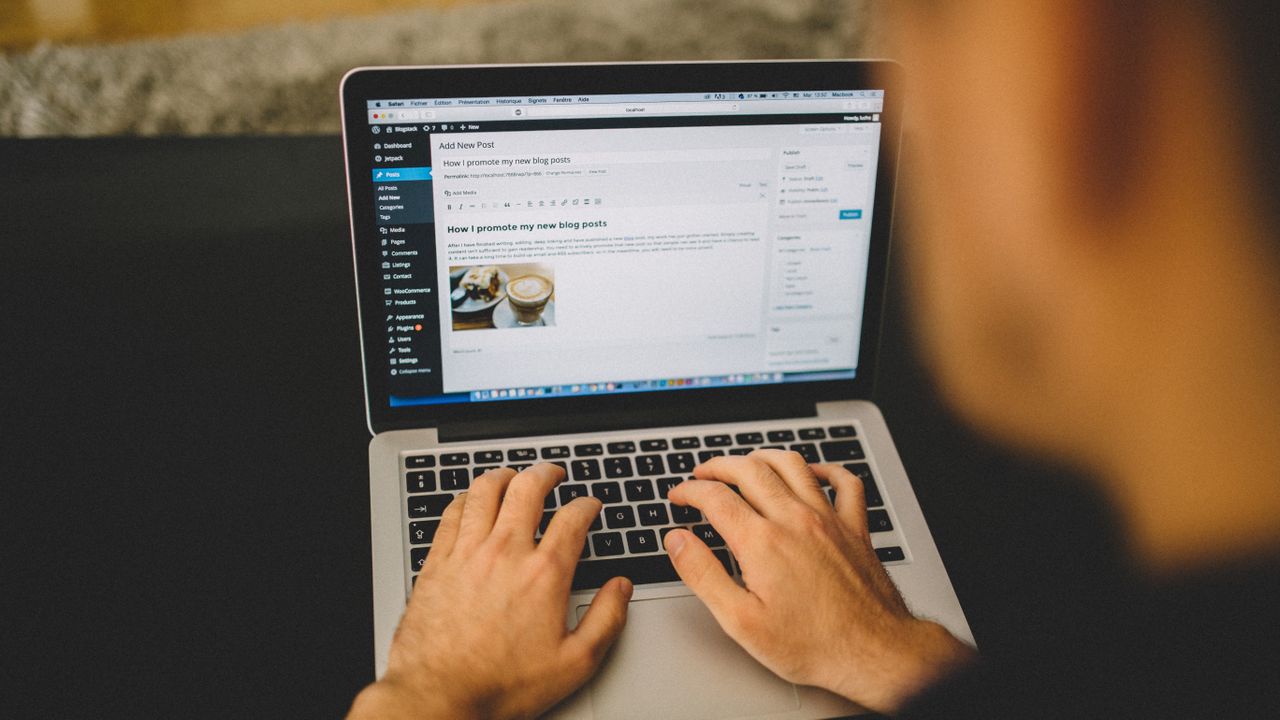
A popular WordPress plugin with hundreds of thousands of active installations carried a vulnerability that allowed threat actors to take over compromised websites, experts have warned.