
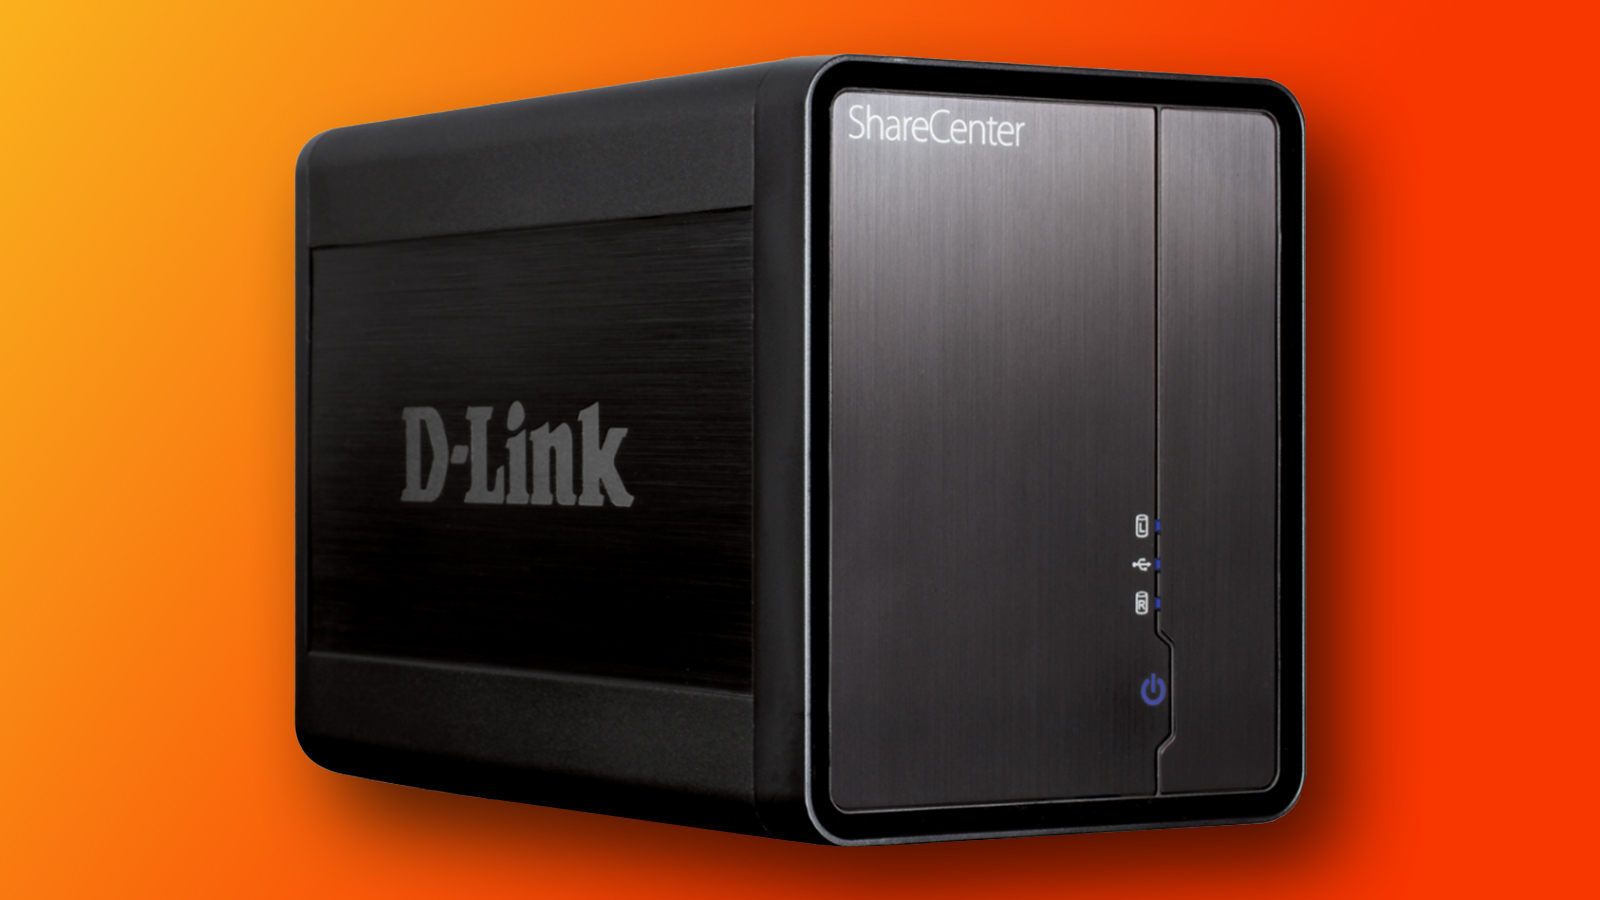
Security researcher Netsecfish discovered a critical flaw in several popular D-Link NAS models that could allow an unauthenticated attacker to execute a command injection attack via an HTTP GET request. According to Netsecfish’s Notion site (h/t BleepingComputer), the vulnerability is in the account_mgr.cgi script, where they could add the malicious input in the name parameter to execute the exploit. This issue is tracked in the National Vulnerability Database (NVD) as CVE-2024-10914 and declared a critical flaw with a severity score 9.2.
The following D-Link models are affected by the issue: DNS-320 Version 1.00, DNS-320LW Version 1.01.0914.2012, DNS-325 Version 1.01, Version 1.02, and DNS-340L Version 1.08.















