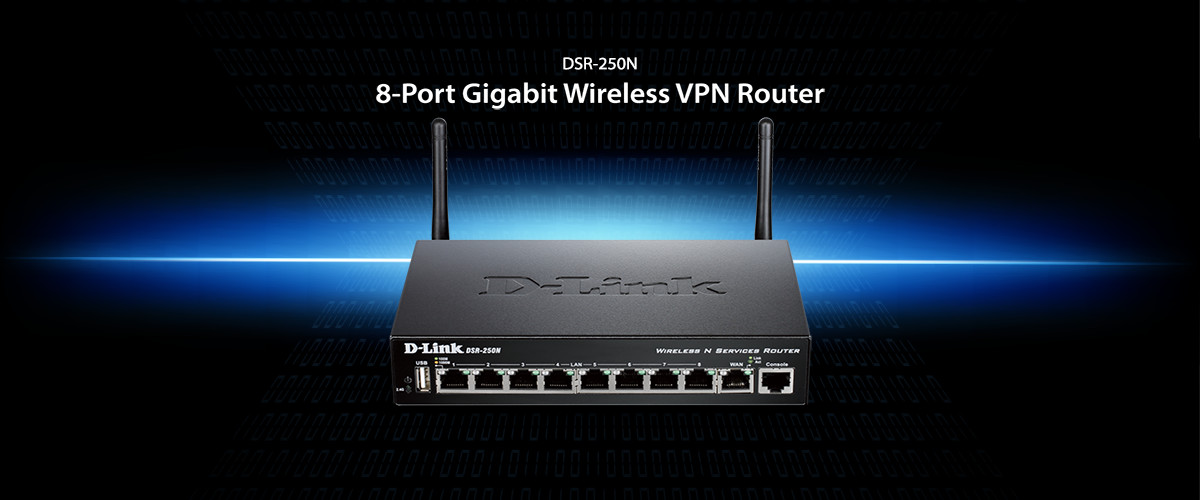
A handful of legacy D-Link routers are susceptible to RCE (Remote Code Execution) threats as the company refuses to offer patches, stating that the devices have reached EOL (End Of Life) and suggests users trash them instead. This report follows a previous incident where D-Link failed to patch over 60,000 NAS devices and recommended users purchase newer models.
Going over the advisory, D-Link says attackers can execute code remotely (RCE) on these routers owing to a stack buffer overflow vulnerability. D-Link didn't share the exact specifics of this threat, possibly to ward off potential hackers. Even so, this unleashes a pandora's box of possible threats, including, but not limited to, data theft, malware and spyware installation, and DoS attacks.