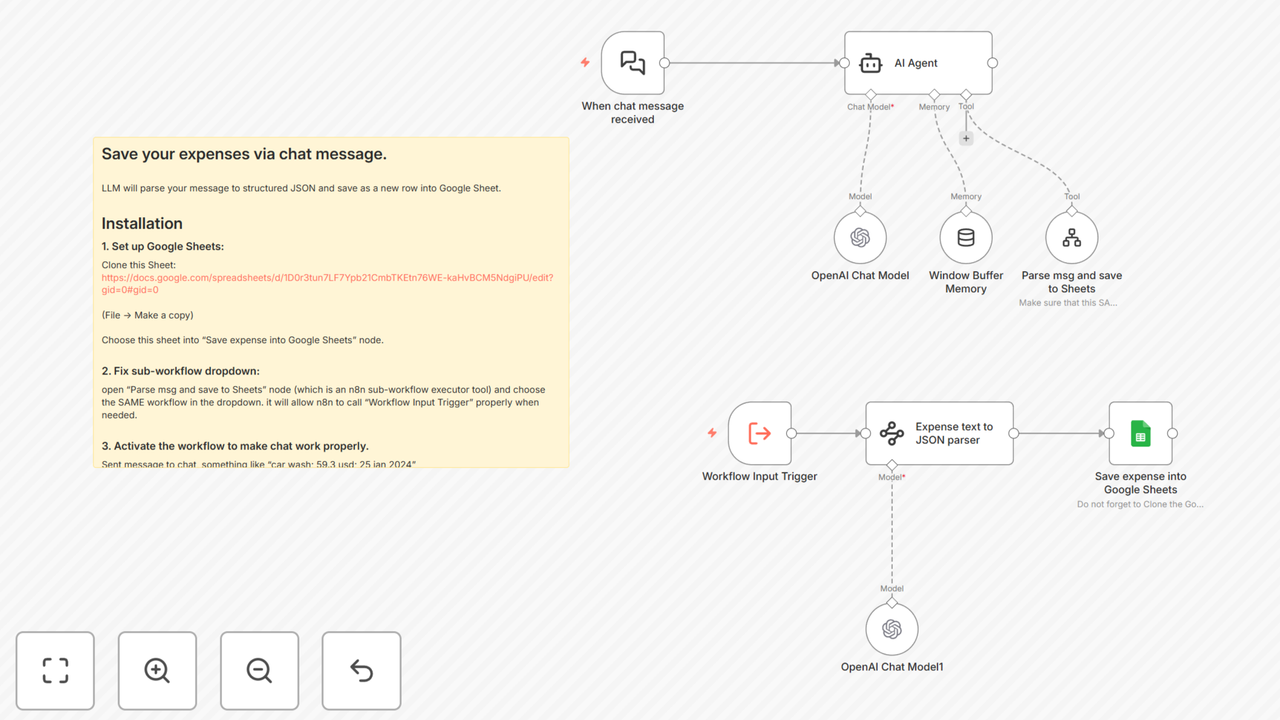
- New flaw in n8n (CVE-2026-25049) allows unauthenticated users to run arbitrary commands on servers
- Vulnerability risks theft of secrets (API keys, OAuth tokens) and cross-tenant data exposure
- Patch released in v2.4.0; PoC already public, making immediate updates critical despite temporary workarounds