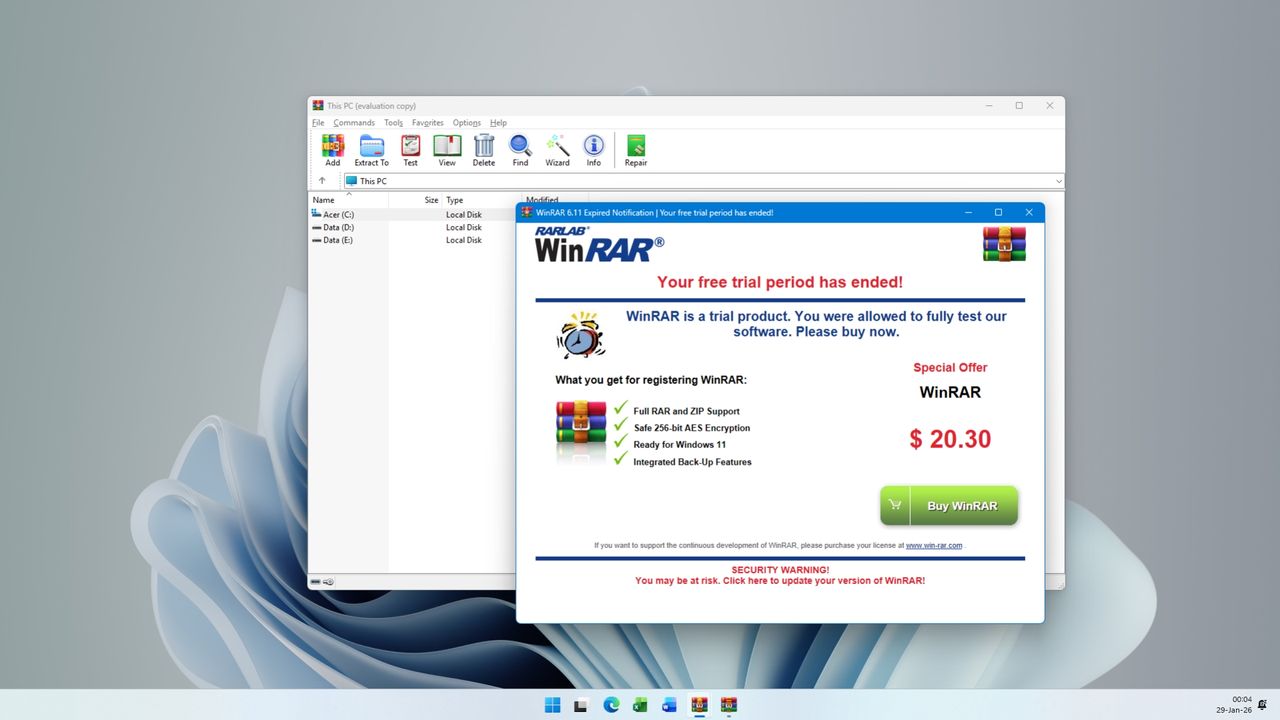
A WinRAR exploit that has been discovered and patched in July 2025 remains widely used by threat actors — many of them government-backed — where a malicious archive delivers its hidden payload to a critical directory like the Windows Startup folder. According to the Google Threat Intelligence Group (GTIG), attackers take advantage of the CVE-2025-8088 critical vulnerability, which has since been addressed with the latest release of WinRAR, version 7.13. However, it seems that users are slow to update their software, as GTIG says that it is still a popular vector used by attackers linked to both China and Russia.
CVE-2025-8088 describes a path traversal vulnerability in earlier versions of WinRAR, in which malicious actors create archives that have a hidden payload. When the victim opens it, the payload is then surreptitiously delivered to a critical path. The Windows Startup folder is often one of the default destinations, ensuring that the delivered malware is executed the next time the user opens or restarts their computer.