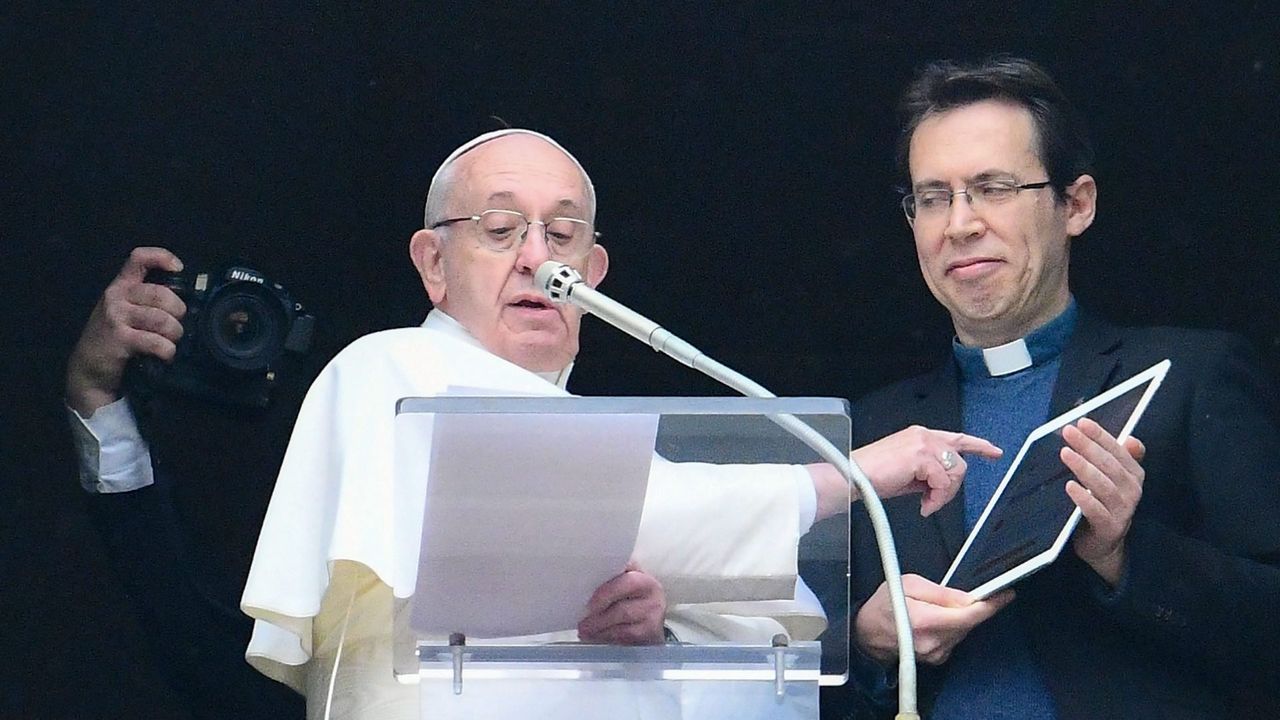
On January 20, 2019, Pope Francis delivered his weekly Angelus to St Peter's Square from a window in the Vatican's Apostolic Palace. In it, he enjoined the faithful to join him on the Church's then-new Click To Pray app—helpfully modelled by a nearby priest, wielding a tablet. Hundreds of thousands of people signed up in the years that followed.
But maybe they shouldn't have, because it turns out the Click To Pray app was, until very recently, absolutely rife with info-leaking security holes. White-hat hacker BobDaHacker revealed in a July 24 blog post (via The Register) that "The Pope's official app exposes 700,000+ user emails." The vulnerability has since been fixed, but it seems only after BobDaHacker went public with their investigation—inquiries made by the hacker and by journalists stretching back to January this year went unanswered.