- Jamf researchers uncover “CrashStealer,” a notarized macOS infostealer disguised as Apple’s CrashReporter
- Distributed via a fake site called “Werkbit Setup”, it bypasses Gatekeeper, installs a LaunchAgent
- It then uses a fake password prompt to unlock Keychain, exfiltrating credentials, cookies, files, and data from 80 crypto wallets and 14 password managers
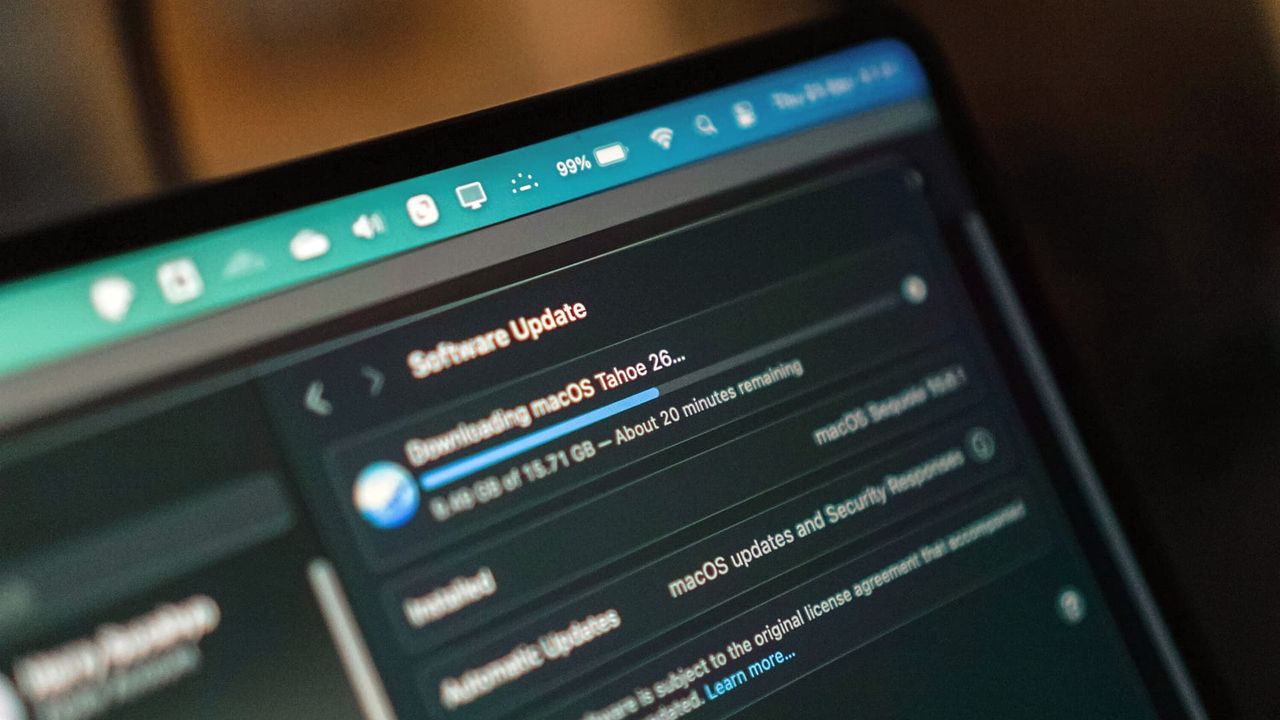
A new macOS infostealer has been spotted in the wild, masquerading as an Apple crash reporting tool, experts have warned.