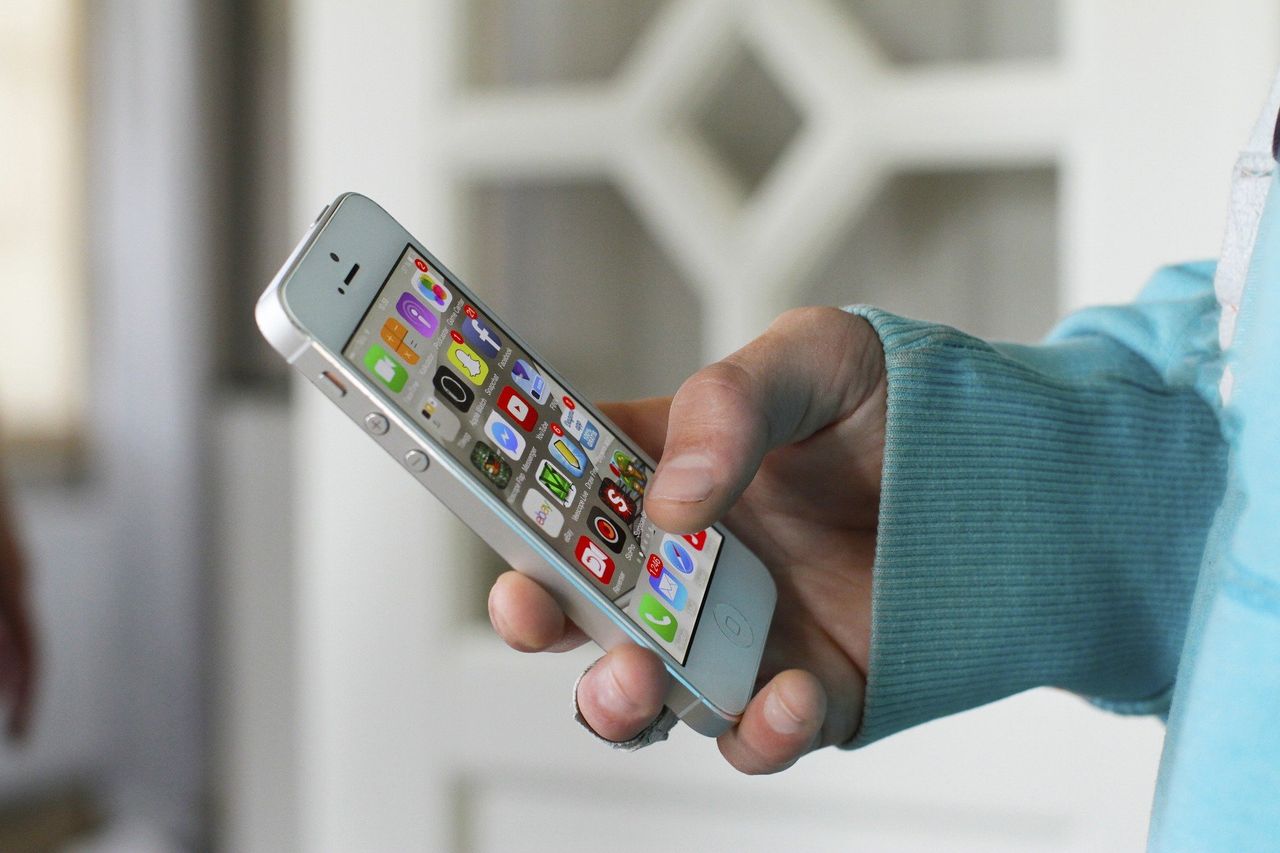
Every mobile app is assembled from layers of code that most security teams never see: third-party libraries, analytics SDKs, advertising frameworks, open-source packages, and proprietary binaries that arrive pre-compiled.
Those apps then run on devices that already contain firmware, chipset software, carrier services, and preinstalled system applications. Each of those components has its own dependencies, update cycles, and security assumptions.