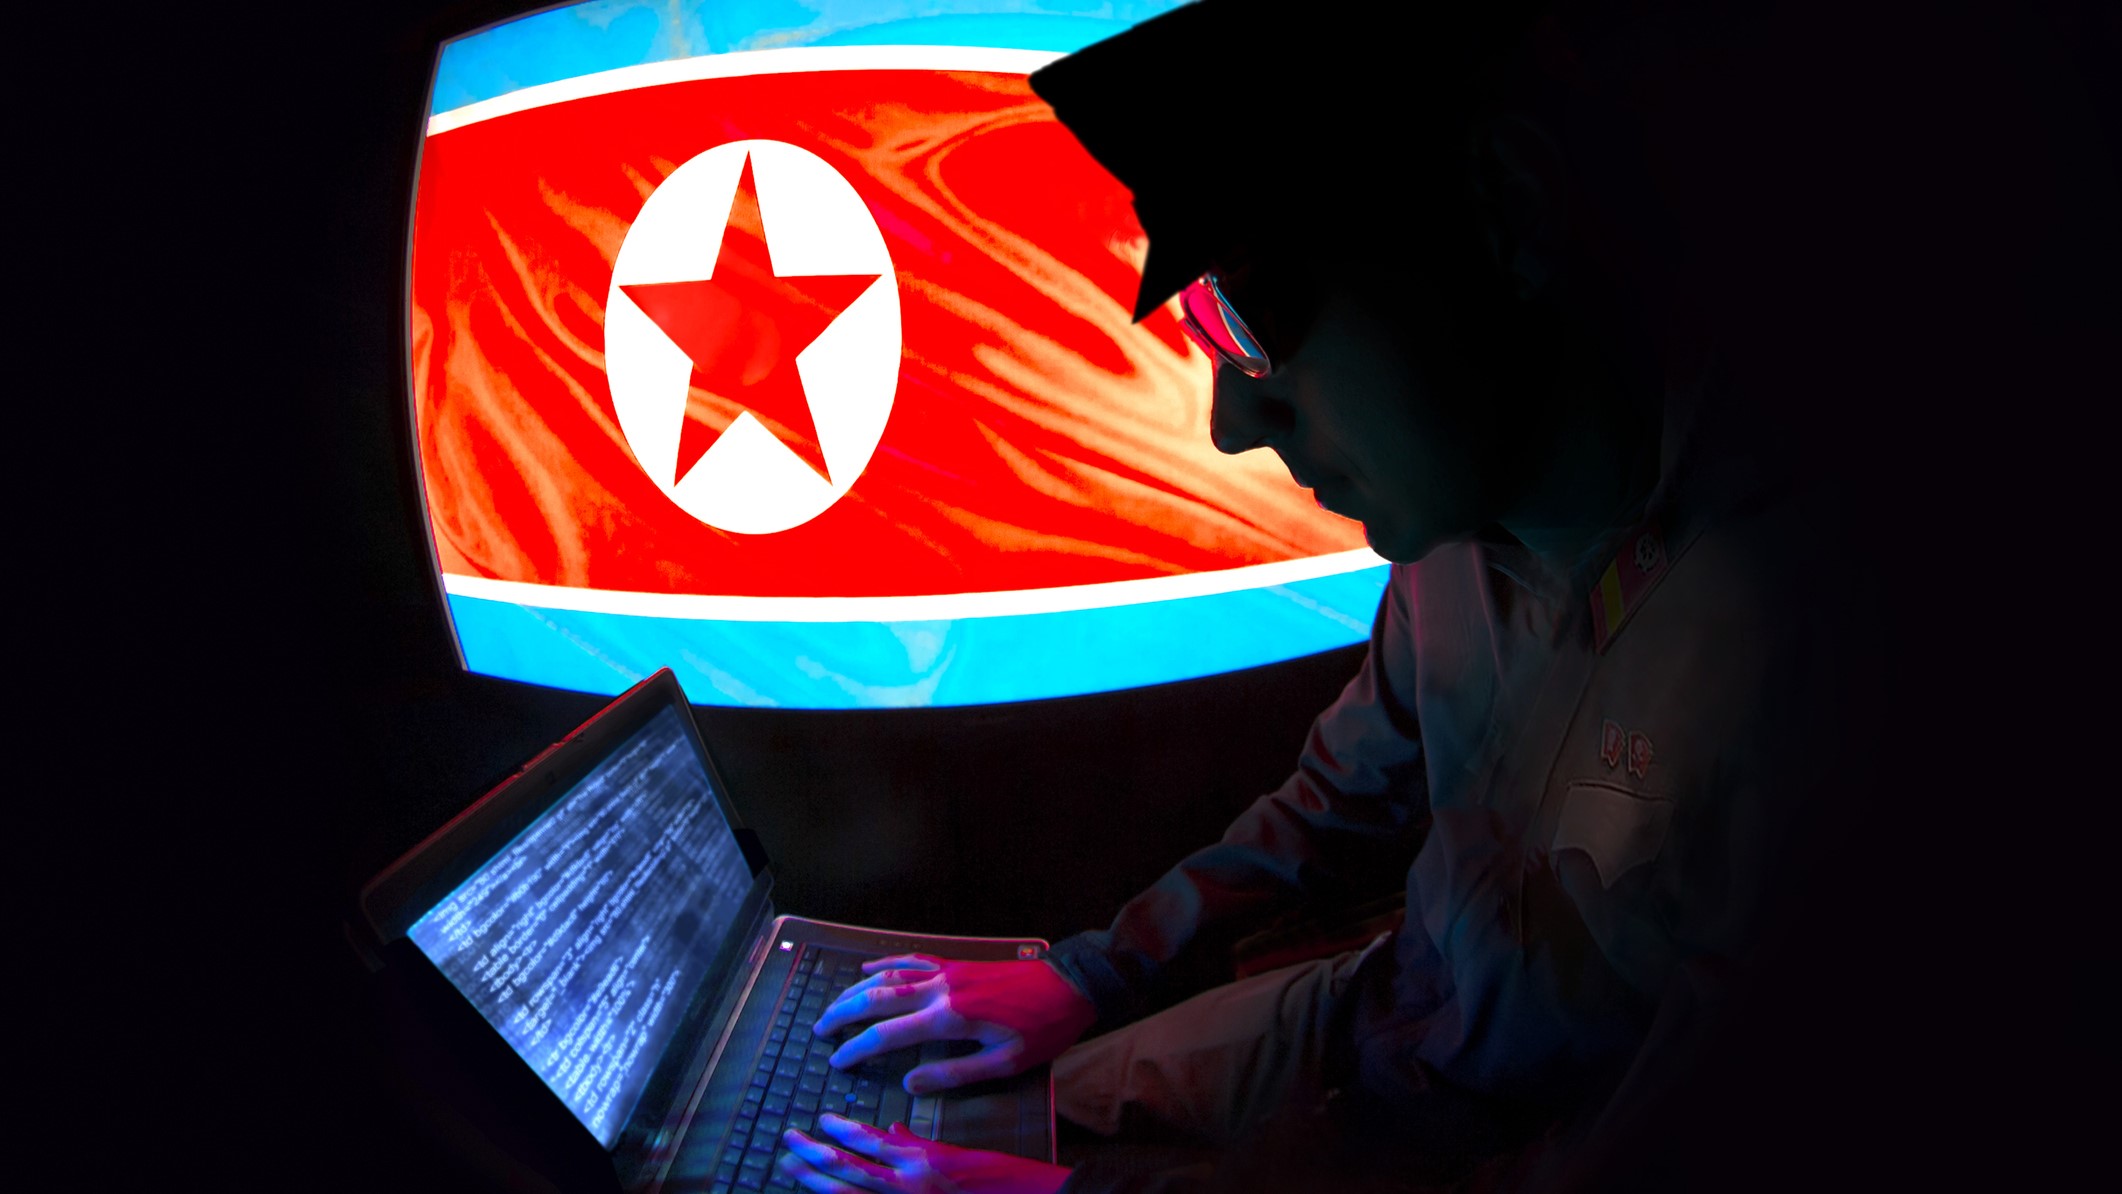
Multiple North Korean state-sponsored hacking groups have been attacking South Korean defense companies for more than a year, stealing login credentials and sensitive data.
A Reuters report, citing South Korea’s law enforcement, claims three major threat actors - Lazarus, Kimsuky, and Andariel, have been going after defense organizations and third-party contractors, planting malicious code in data systems, pulling out passwords and technical information.