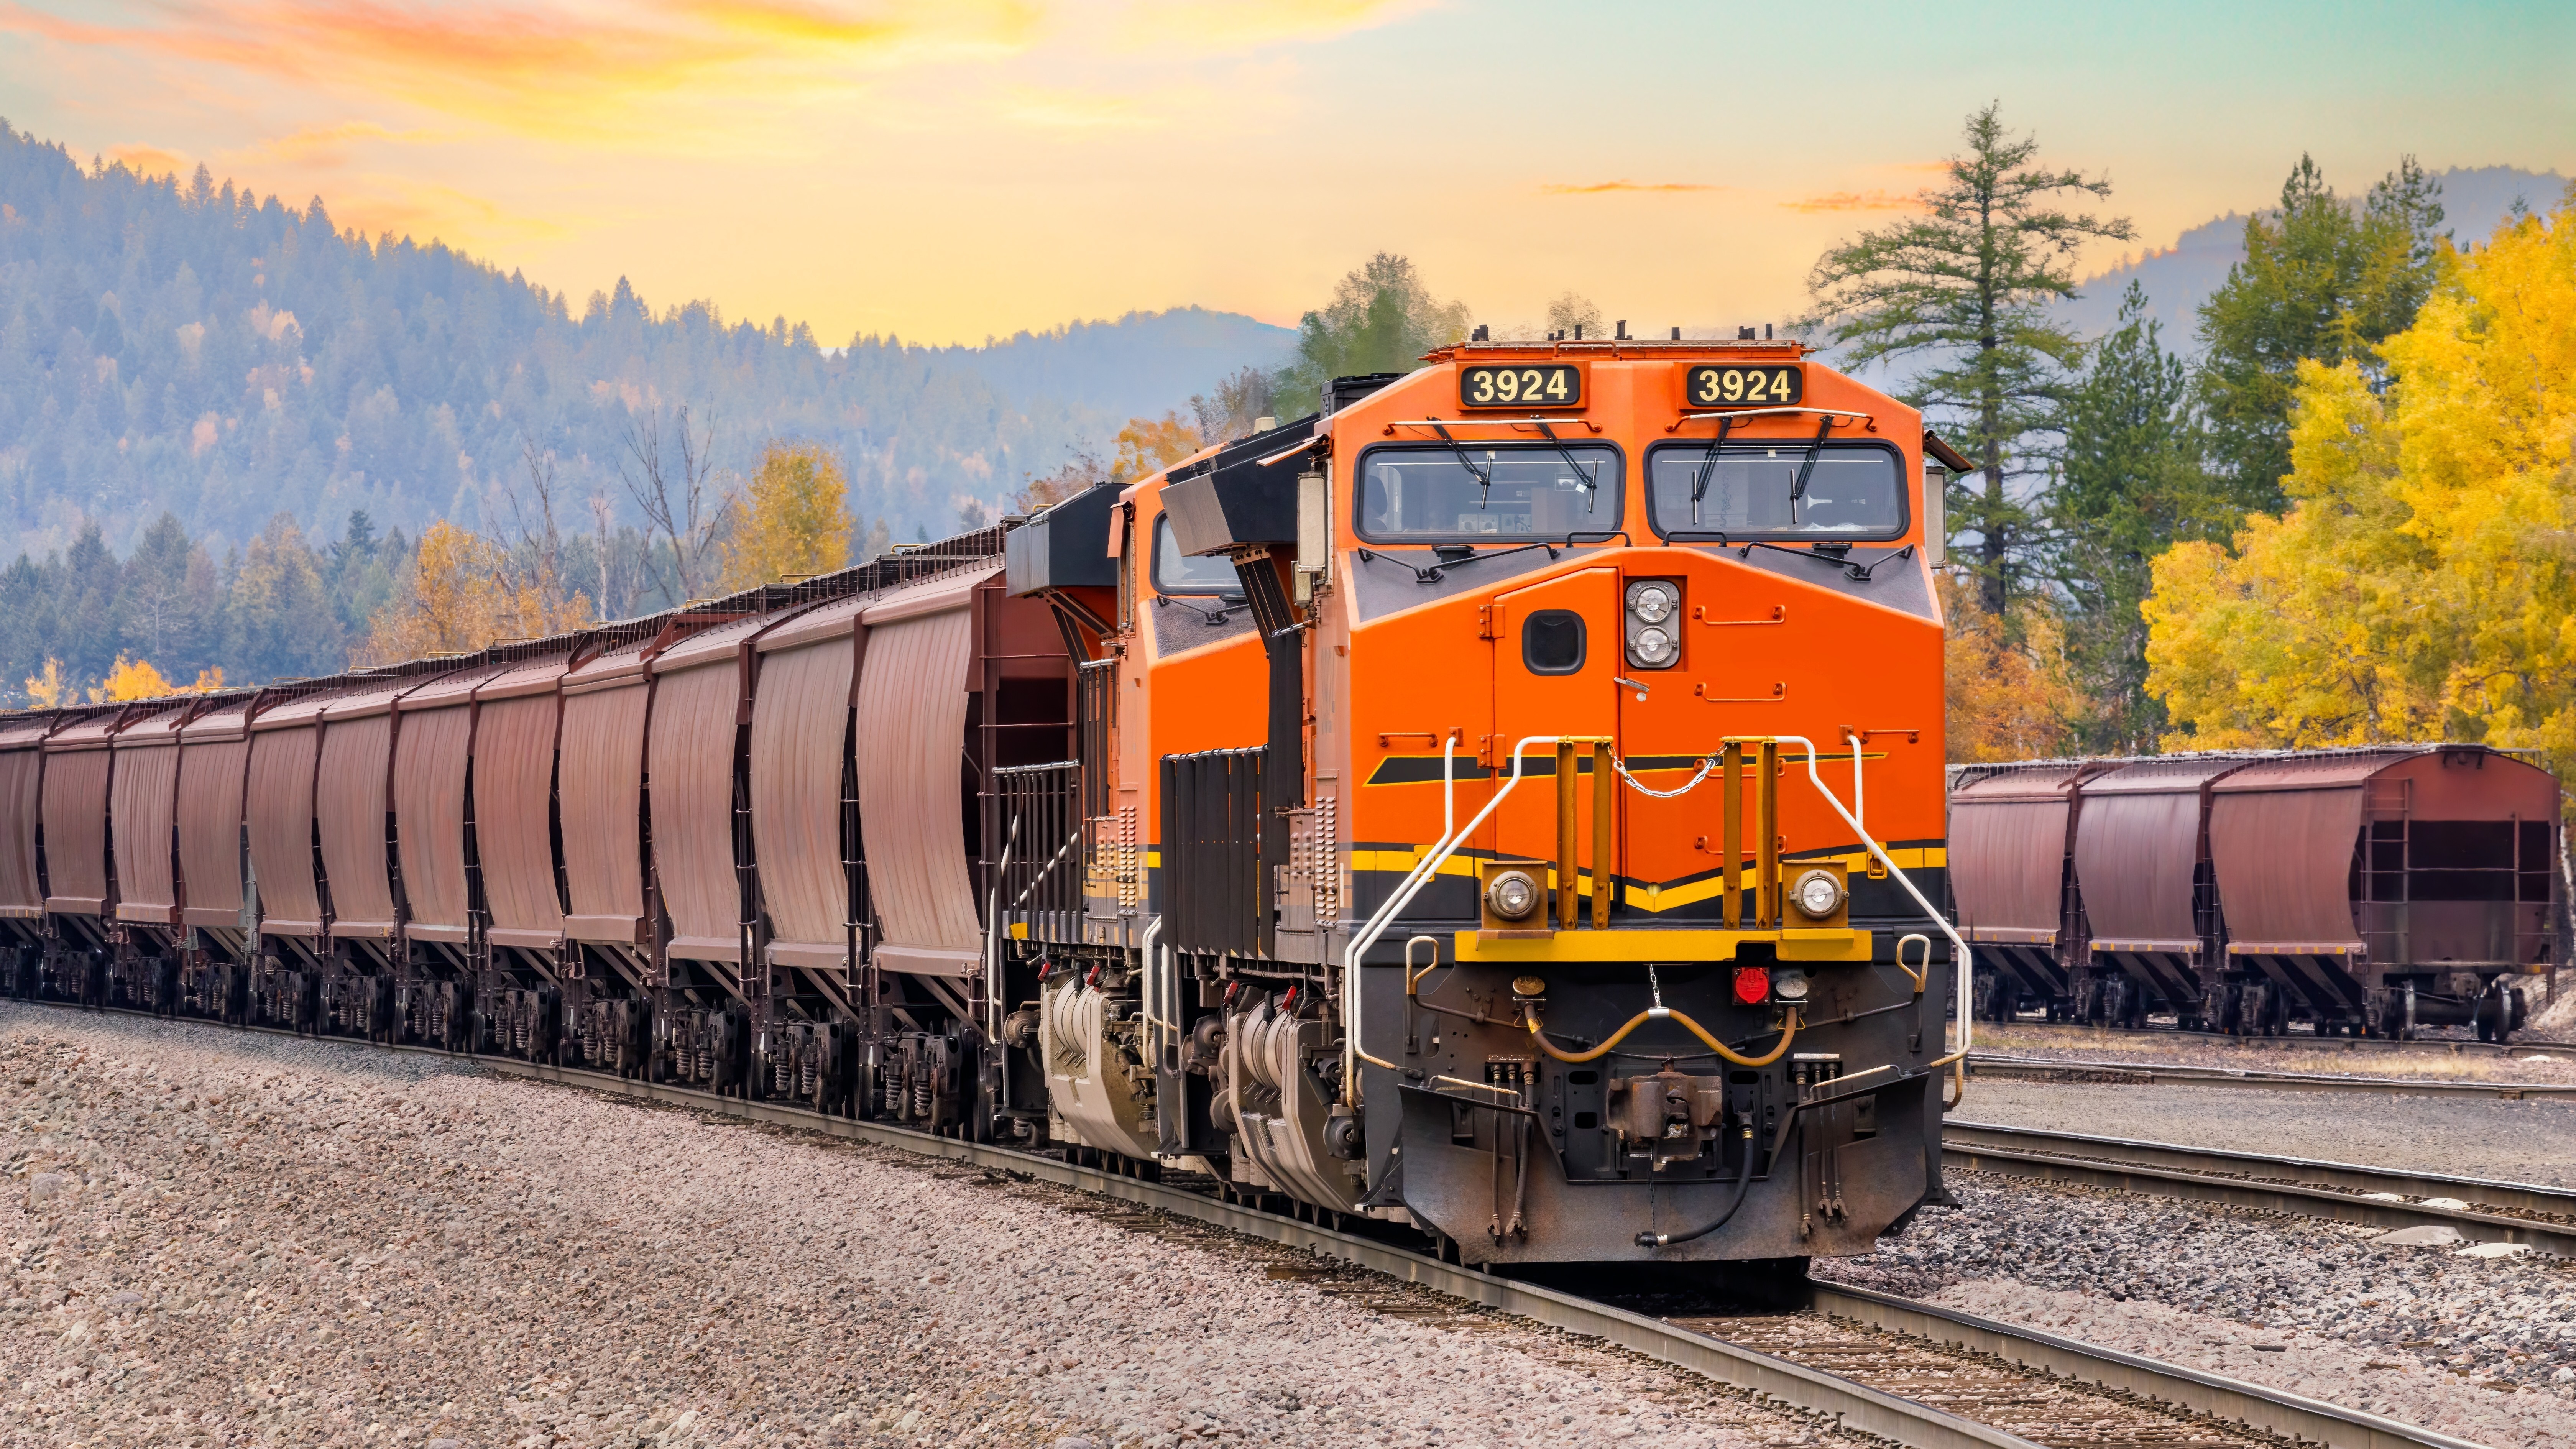
A security vulnerability on American trains was discovered in 2012, but the American Association of Railways (AAR) has refused to act on it until the Cybersecurity & Infrastructure Security Agency (CISA) published an advisory a few days ago. According to Hardware Security Researcher Neils on X (formerly Twitter), they first discovered the issue in 2012 when software-defined radios (SDR) started becoming more popular. All American trains were equipped with an End-of-Train (EoT) module attached to the last carriage, which reports telemetry data to the front of the train wirelessly.
Turns out you can just hack any train in the USA and take control over the brakes. This is CVE-2025-1727 and it took me 12 years to get this published. This vulnerability is still not patched. Here's the story: https://t.co/MKRFSOa3XYJuly 11, 2025