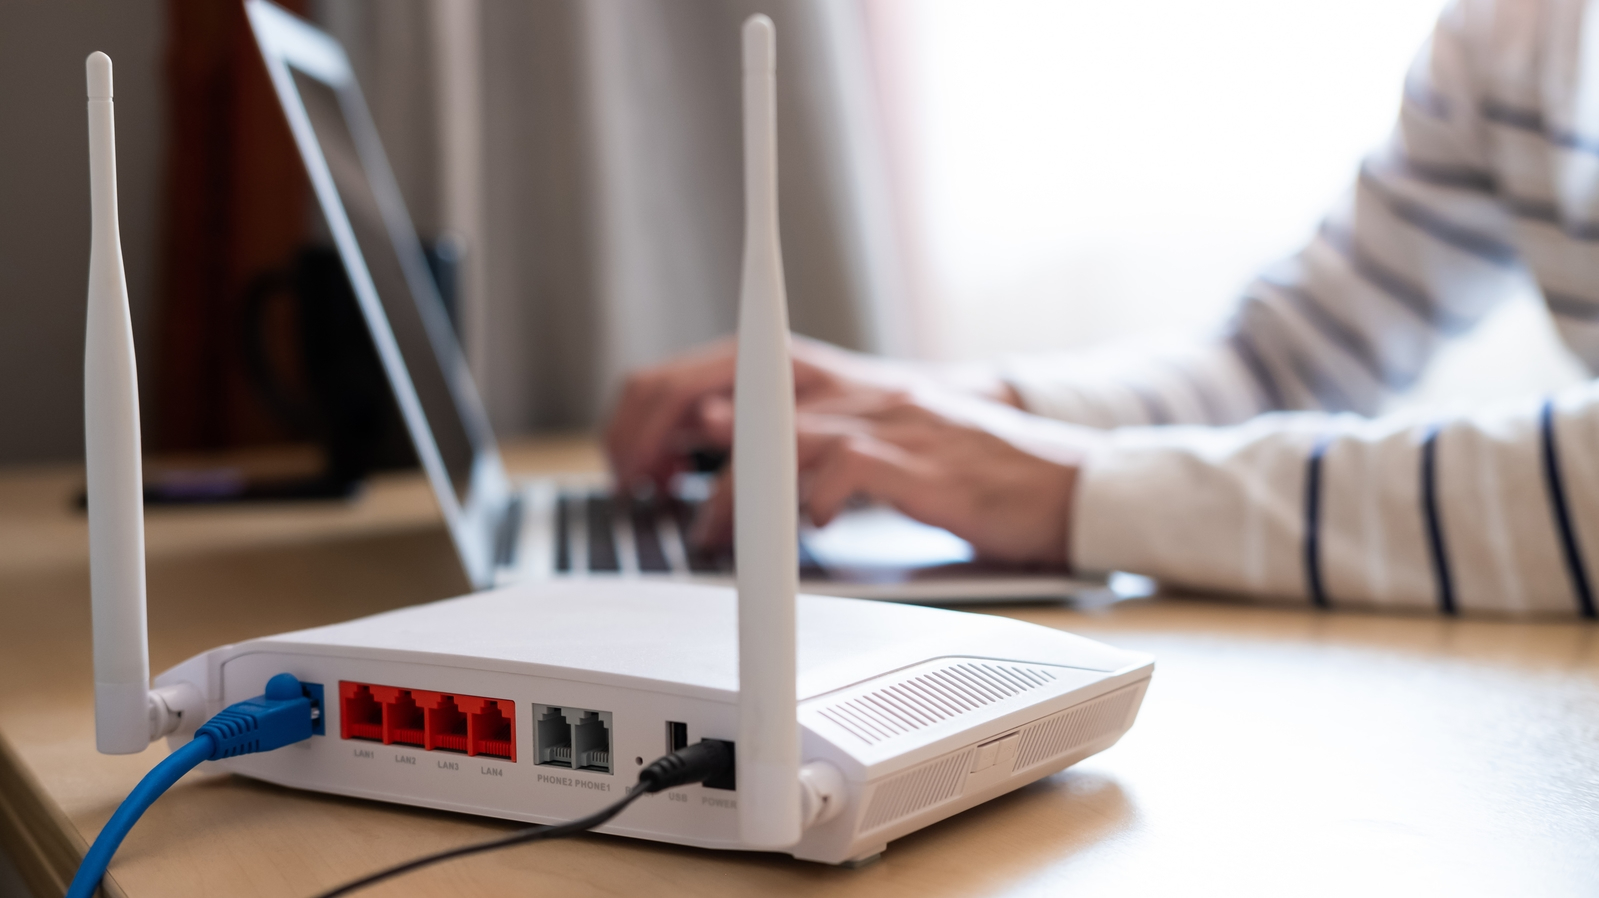
GRU-funded hacking team Fancy Bear has been caught installing Moobot malware on "well over a thousand" unsecured home and business routers using the default admin password as the infection vector, says FBI Director Christopher Wray [h/t The Register].
Moobot was used to create a functional botnet of compromised routers that the GRU and Fancy Bear were using for undisclosed reasons, but the scale of the security breach isn't promising. The FBI acted to isolate and remove the malware from all infected units. The issue stems from a lack of cybersecurity basics (change the admin password unless you want someone else to change it for you) taught to the public. So, it's not quite like a hardware vulnerability that can't be fixed without revision.