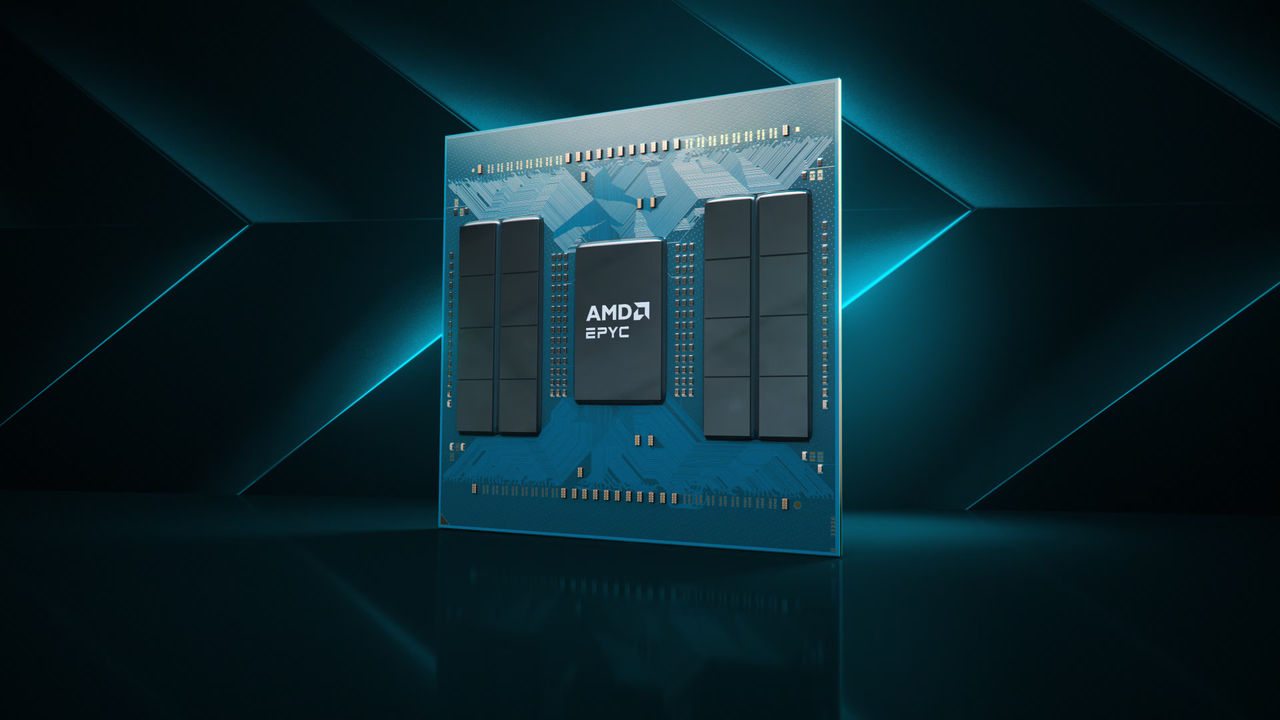
Researchers at ETH Zurich disclosed a software-only vulnerability in April that silently undermines AMD SEV-SNP confidential computing protections on AMD's EPYC platforms, giving a malicious cloud host full read and write access to supposedly protected virtual machine memory. The technique, dubbed “Fabricked,” exploits flaws in how the CPU's Infinity Fabric interconnect handles memory routing during boot — and can forge the cryptographic attestation reports tenants rely on to verify their environment hasn't been tampered with.
The researchers presented the findings as part of a USENIX Security 2026 paper, describing the exploit as fully deterministic with a 100% success rate, without a need for physical access and no code execution inside the victim VM.