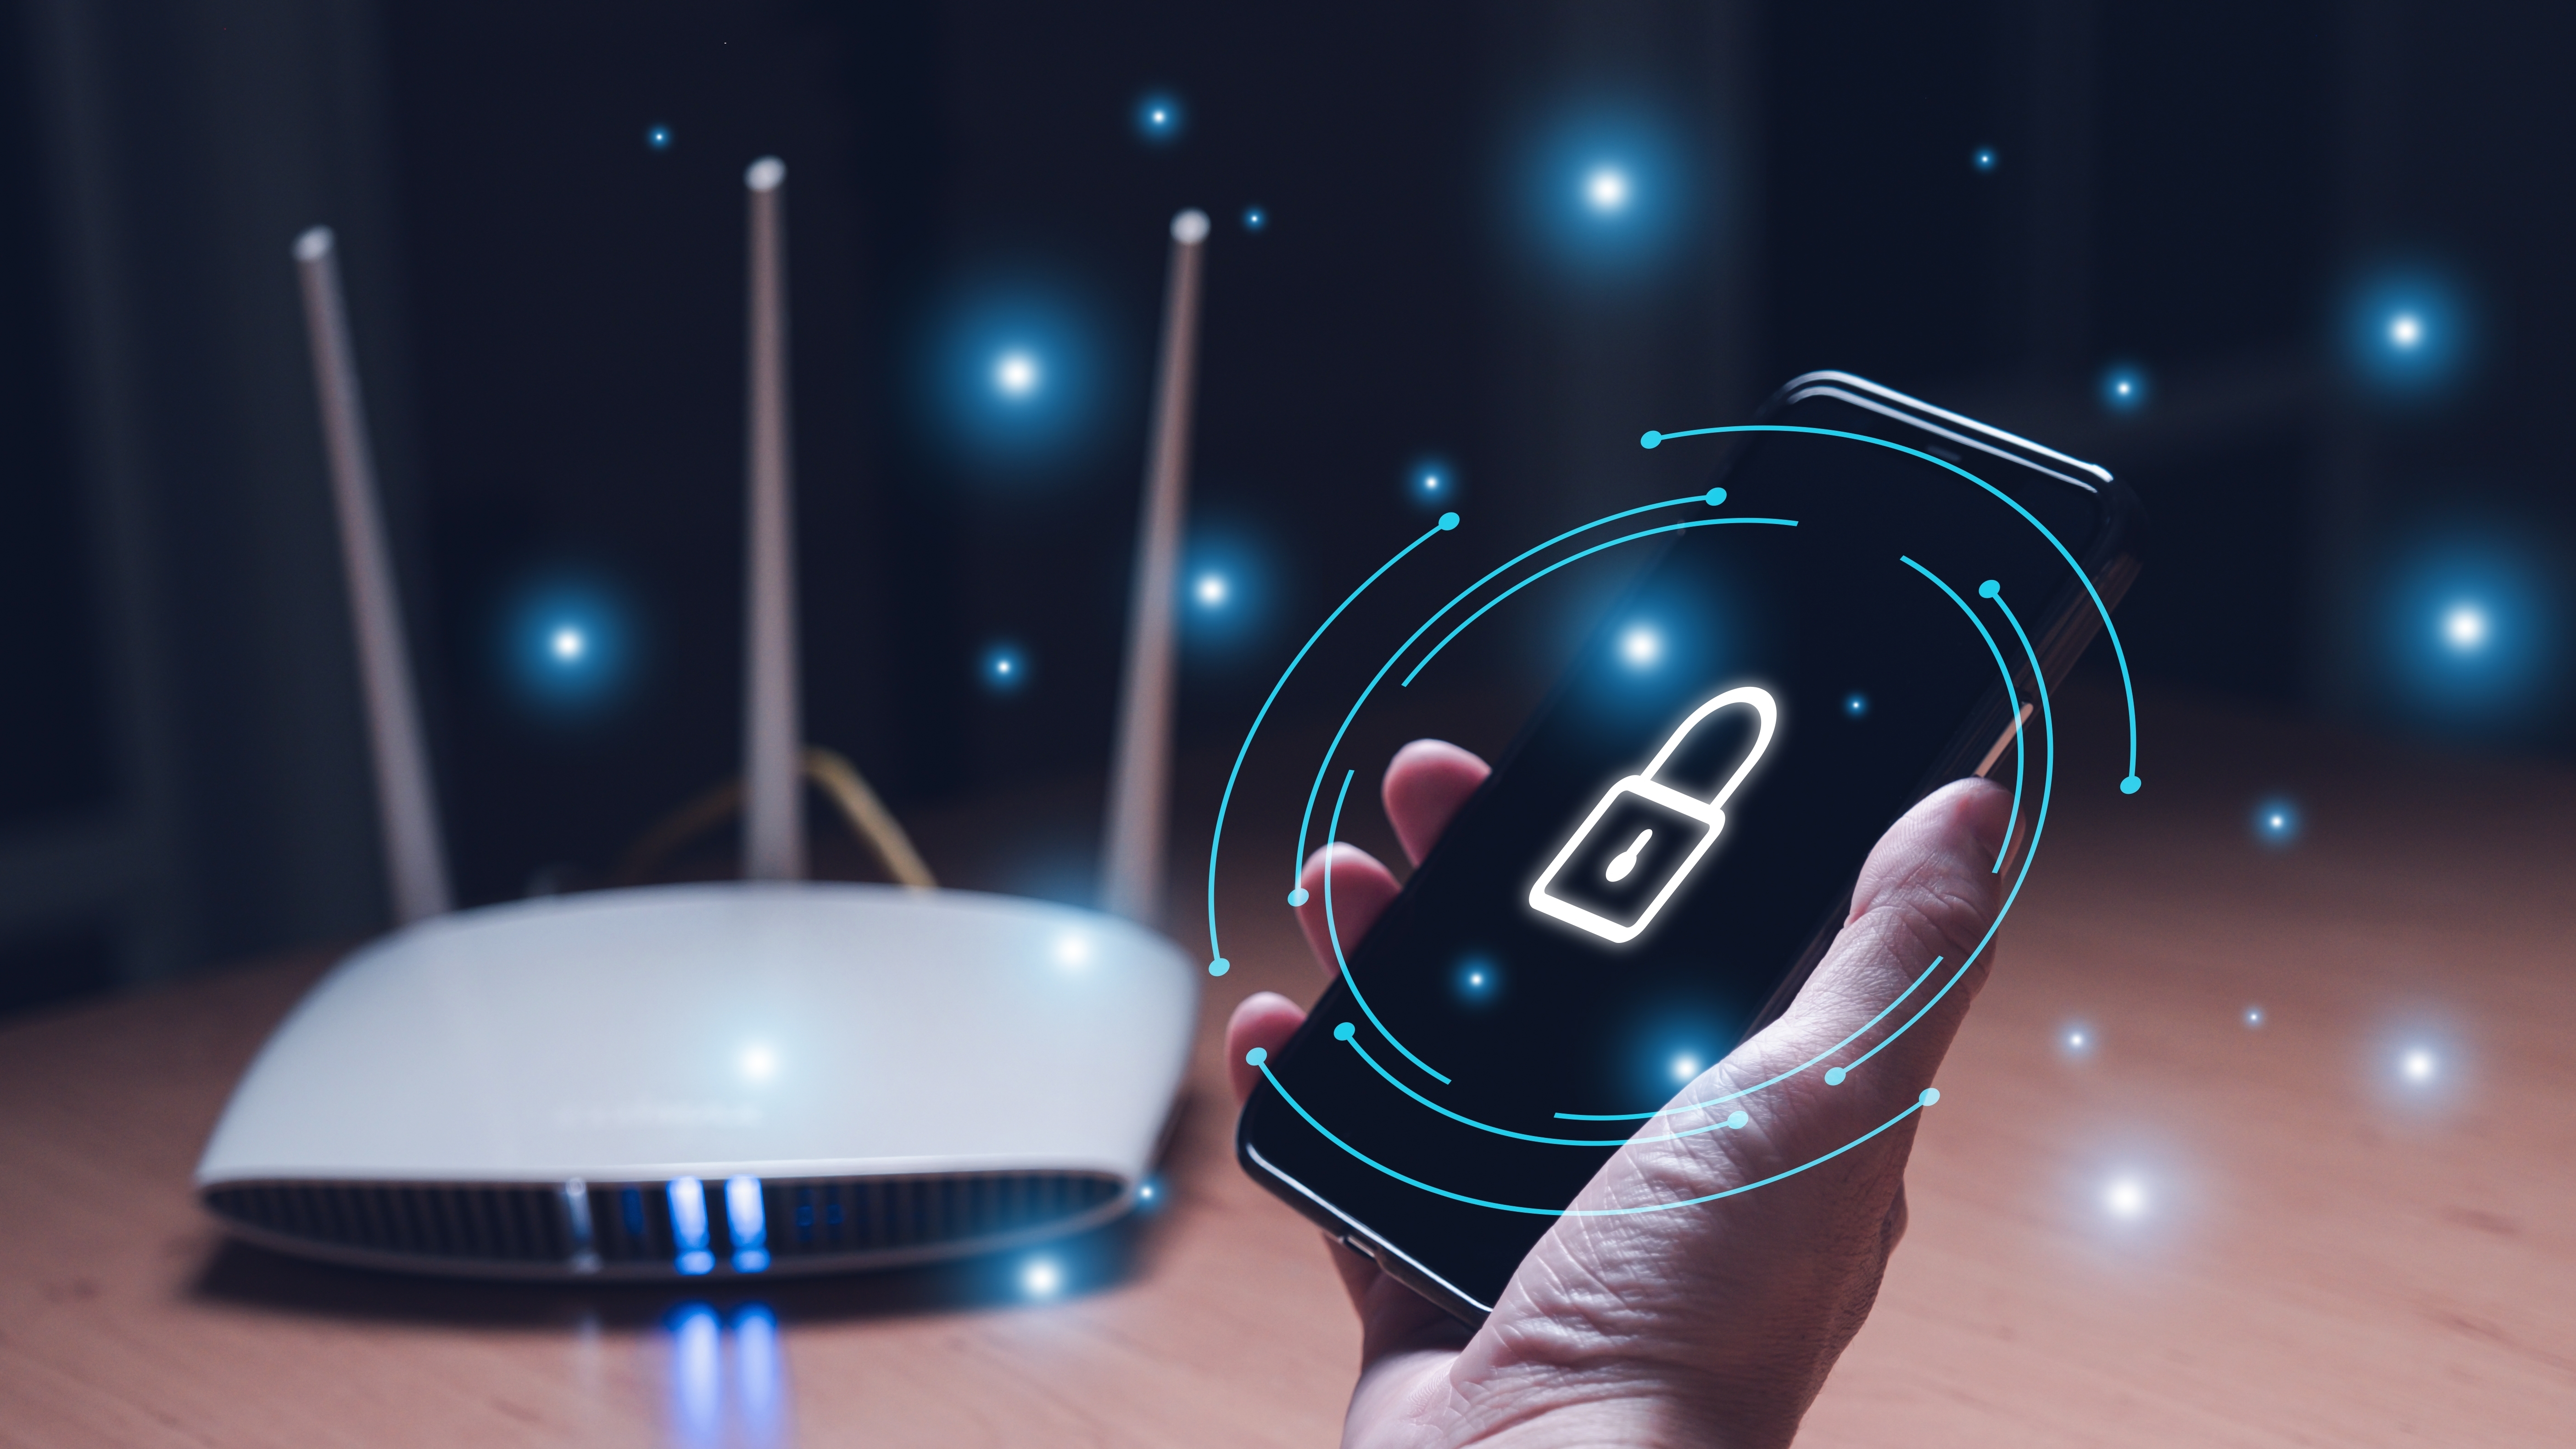
The most popular brand of router in Russia, MikroTek, has been compromised by cybercriminals with links to Russia in order to send spoofed emails and deliver trojan malware. Infoblox researchers have discovered a large-scale botnet operation that turns misconfigured routers into zombie botnets, with at least 13,000 compromised routers acting as proxies for the malware.
The hackers chose servers with DNS misconfigurations, then spoofed spam using a massive network of relays – this being the 13,000 compromised routers configured as SOCKS proxies. When a compromised proxy forwards traffic without checking the origin, the recipient can’t check to see if it’s coming from an original source so malicious emails seem to originate from legitimate domains and are able to bypass protections.