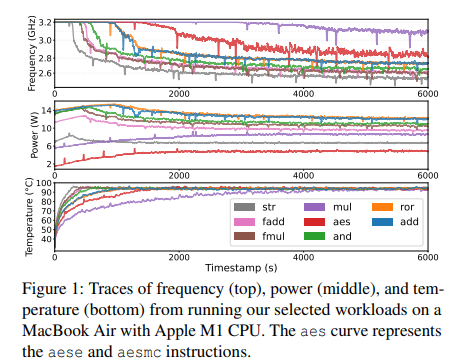
A team of security researchers funded in part by DARPA and the US Air Force has demonstrated tactics that allowed them to steal data from Arm CPUs from Apple and Qualcomm, and also from discrete GPUs from Nvidia and AMD and integrated graphics in Intel and Apple chips, by monitoring chip temperature, power, and frequency during normal operation. The attack requires data from the PC's internal power, temp, and frequency sensors, but this information can be accessed from local user accounts that don't have administrator access. In this manner, an unprivileged user could gain access to privileged data.
The researchers' current attack methods serve as a proof of concept, but luckily data exfiltration rates are very low with the current method, and if a user had direct access to the system, such as required here, they would likely target easier attack surfaces. However, the researchers note that further work could speed up the process, and this is typically how a broad class of attacks begin to be exploited -- a proof of concept proving that the tactic works, and then rapid acceleration by other researchers and/or nefarious actors.
The researchers' paper, 'Hot Pixels: Frequency, Power, and Temperature Attacks on GPUs and Arm SoCs [PDF],' demonstrates using a side-channel attack, which is a type of attack that allows exfiltrating data by measuring certain physical emissions of a computer.
In this case, the researchers leveraged the information exposed by the Dynamic Voltage and Frequency Scaling (DVFS) mechanism that is present on nearly all modern chips. DVFS modulates frequency and power in real-time to keep heat and TDP at acceptable levels, therefore unlocking either the best power efficiency or the best performance for the currently running task on the processor. This is controlled by the chips' P-state, which the researchers used to gather data.
By forcing one of the three variables of DVFS (heat, power, or frequency) to become a constant, the researchers can then monitor the other two variables to distinguish which instructions are being executed, even with enough precision to ascertain the different operands of the same instruction.
Ultimately, this furthers other attack methods, like website fingerprinting. Additionally, by monitoring frequency throttling via a Javascript code running in a browser, the researchers used pixel-stealing and history-sniffing attacks with the latest versions of Chrome and Safari despite all side-channel mitigations being enabled.