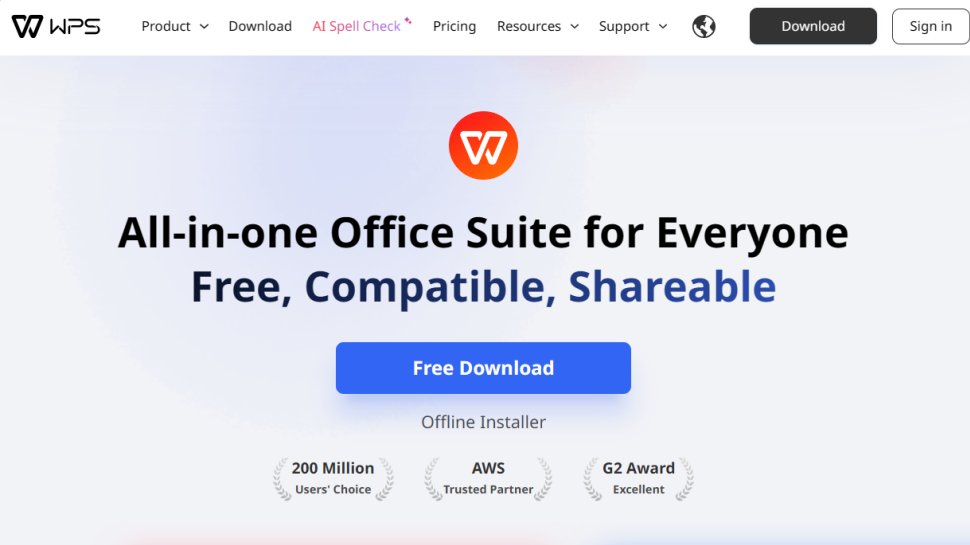
The popular WPS Office workplace productivity software suite carried a vulnerability which allowed some threat actors to deploy backdoors to their target’s endpoints, experts have claimed.
Cybersecurity researchers at ESET found WPS Office was vulnerable to an improper path validation flaw, tracked as CVE-2024-7262. It carries a severity score of 9.3 (critical), and impacts multiple versions (from 12.2.0.13110, to 12.1.0.16412). The first patch to address the issue came out in March 2024, but some threat actors were allegedly already exploiting it a month earlier.