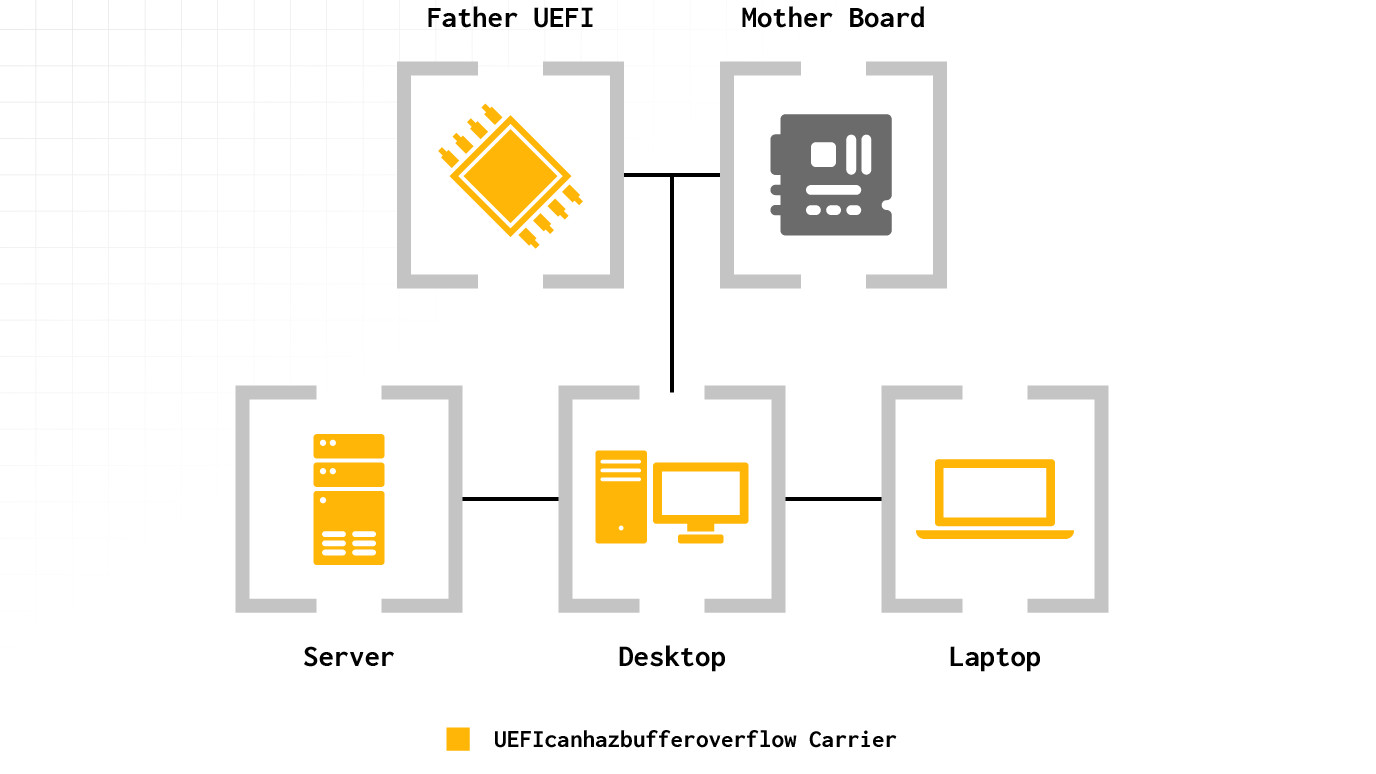
Using its automated binary analysis system Eclypsium Automata, Eclypsium has uncovered the existence of high-impact security vulnerabilities in Phoenix SecureCore UEFI firmware used by a wide variety of motherboard providers and Intel CPUs spanning from 14th Gen to 6th Gen—all the "Lakes" in other words. This vulnerability also extends to several other UEFI BIOS vendors, including Lenovo, Intel, Insyde, and AMI. Phoenix is the latest to join the list.
The specific Phoenix SecureCore UEFI firmware vulnerability that prompted this posting is referred to as "UEFIcanhazbufferoverflow" by Eclypsium, which is just a funny way of pointing out that this is a buffer overflow exploit. The specific method in which the "UEFIcanhazbufferoverflow" exploit works is by using an unsafe call to the "GetVariable" UEFI service.