- CoPhish uses Copilot Studio agents to phish OAuth tokens via fake login flows
- Attackers exploit Microsoft domains to appear legitimate and access sensitive user data
- Mitigations include restricting app consent, enforcing MFA, and monitoring OAuth activity
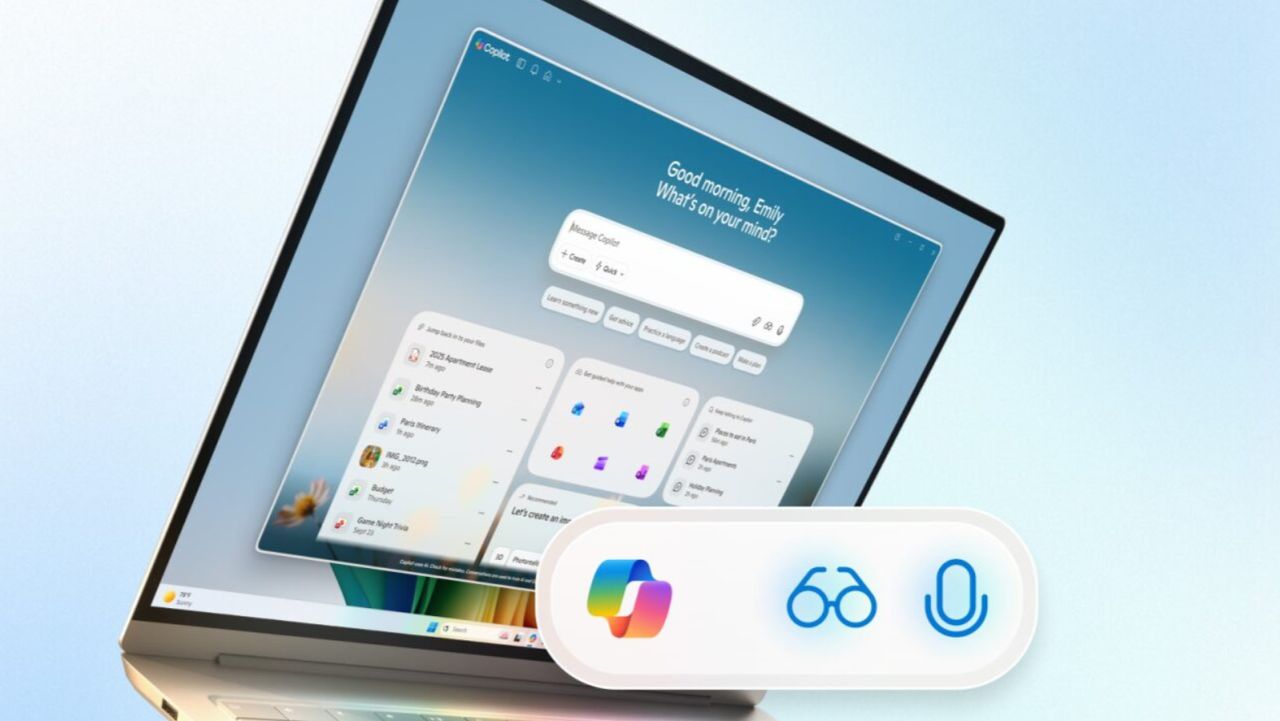
Security researchers from Datadog Security Labs are warning about a new phishing technique weaponizing Microsoft Copilot Studio agents to steal OAuth tokens and grants attackers access to sensitive information in emails, chats, calendars, and more.