Bulgaria, France, Ireland, Luxembourg, the Netherlands, Portugal, Spain, Sweden have all yet to adopt cybersecurity rules for critical sectors almost a year after an EU deadline, according to the latest data, meaning they face potential legal action.
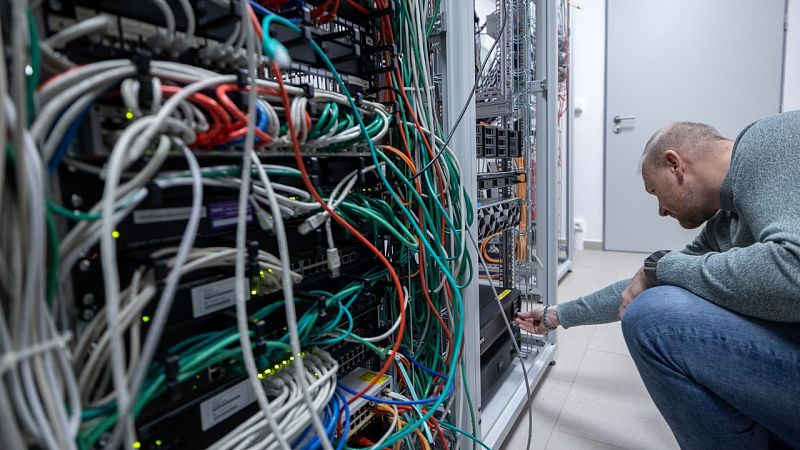
The Network and Information Security Directive 2 (NIS2), which was approved back in 2022 aims to protect critical entities, such as energy, transport, banking, water and digital infrastructures, against major cyber incidents.