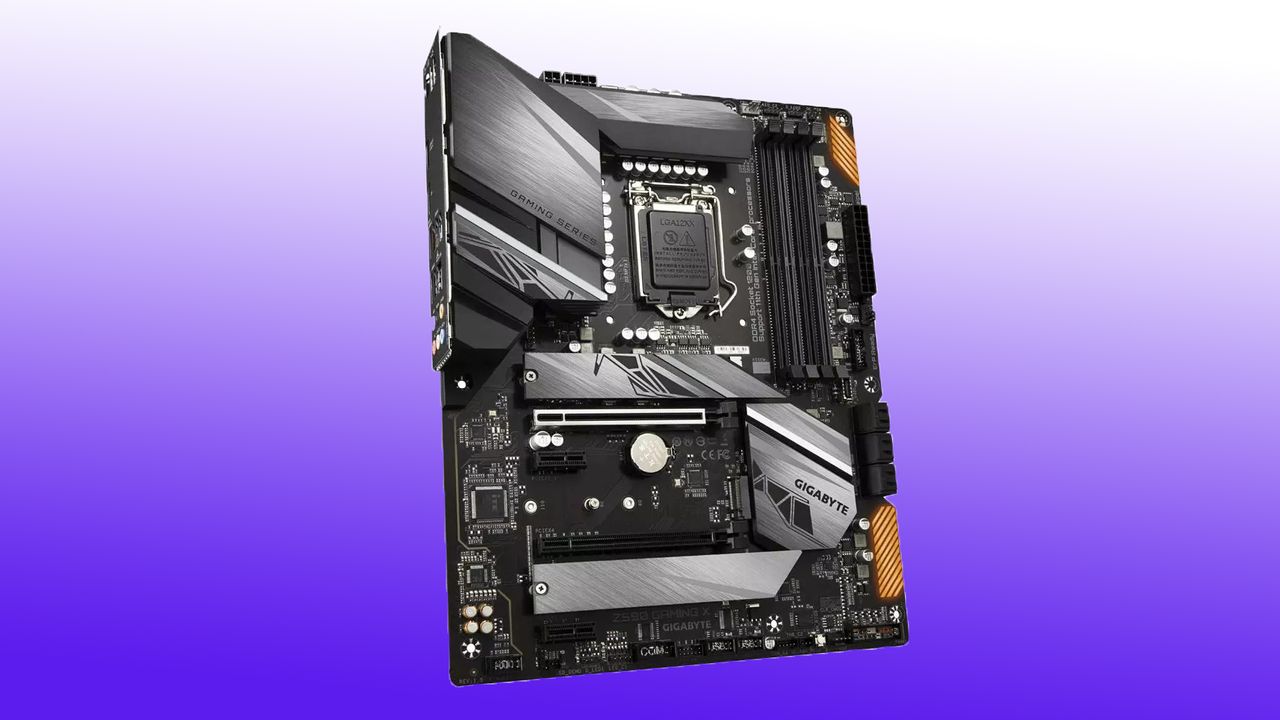
Firmware security research company Binarly has discovered four new vulnerabilities affecting the UEFI (Unified Extensible Firmware Interface) on multiple Gigabyte motherboards. The vulnerabilities with CVE identifiers CVE-2025-7029, CVE-2025-7028, CVE-2025-7027, and CVE-2025-7026 were shared with Carnegie Mellon University’s CERT Coordination Center (CERT/CC) for further analysis.
The cause of concern is said to lie within the System Management Mode (SMM), a high-privilege operating mode on x86 processors meant for low-level system management tasks. SMM grants UEFI access to the system hardware, where all the code is executed in a secure memory area called System Management RAM (SMRAM). This memory can only be accessed using Special System Management Interrupt (SMI) handlers, which rely on specific communication buffers to process data. However, in case these handlers do not validate the data, it can potentially allow an attacker to execute arbitrary code before the operating system is loaded.