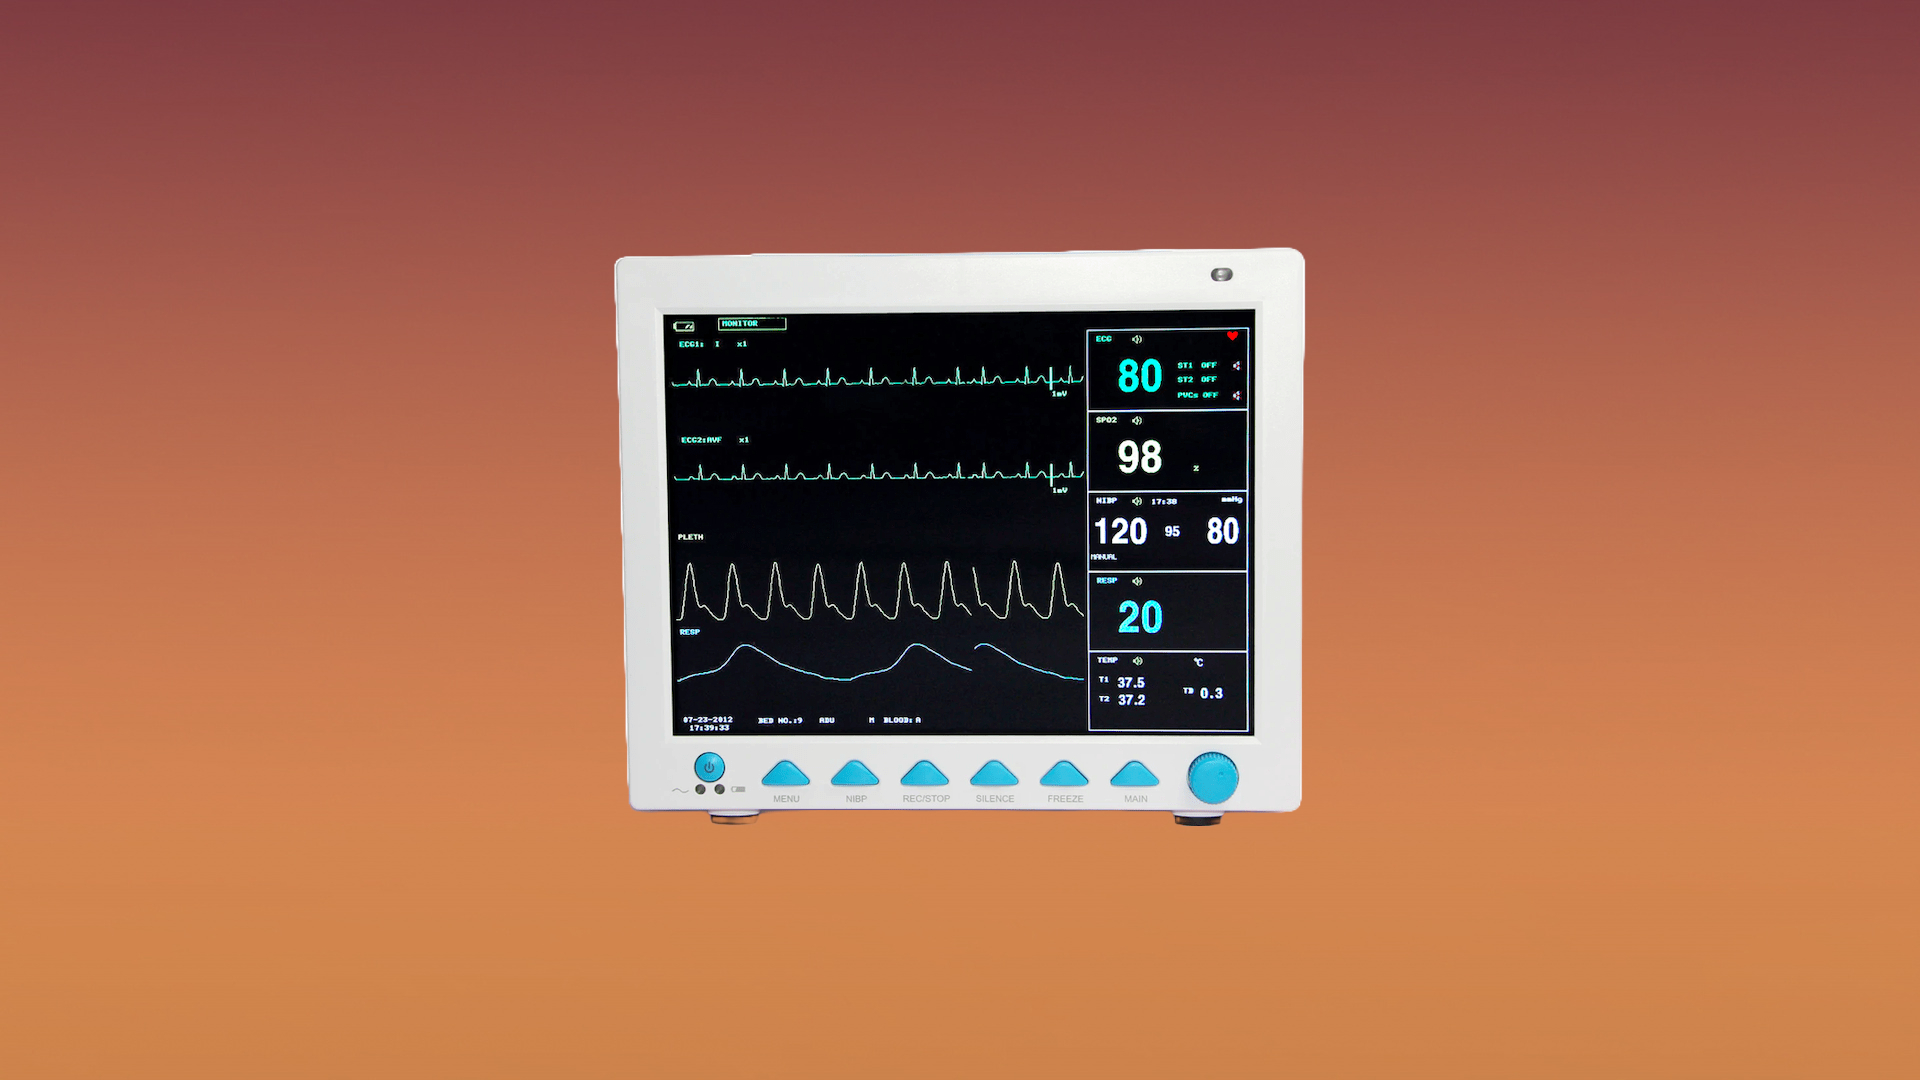
The US-based Cybersecurity & Infrastructure Security Agency recently released an investigation report involving three firmware versions used in a patient monitoring system called Contec CMS8000, used in hospitals and healthcare facilities. It was discovered that these devices had a backdoor with a hard-coded IP address, allowing the patient data to be transmitted. This is possible as the devices will enable a connection to a central monitoring system via a wired or wireless network, according to the product description.
The agency revealed the codes that transmit data to a particular IP address. This decoded data contains detailed information, such as the doctor's name, patients, hospital department, admission date, date of birth, and other information about the people who used this device. This vulnerability is filed under CVE-2025-0626 with a CVSS v4 score of 7.7 out of 10. Two other vulnerabilities were filed under CVE-2024- 12248, which indicates that it could allow an attacker to write data remotely to execute a code, and CVE-2025-0683, which relates to privacy vulnerability.