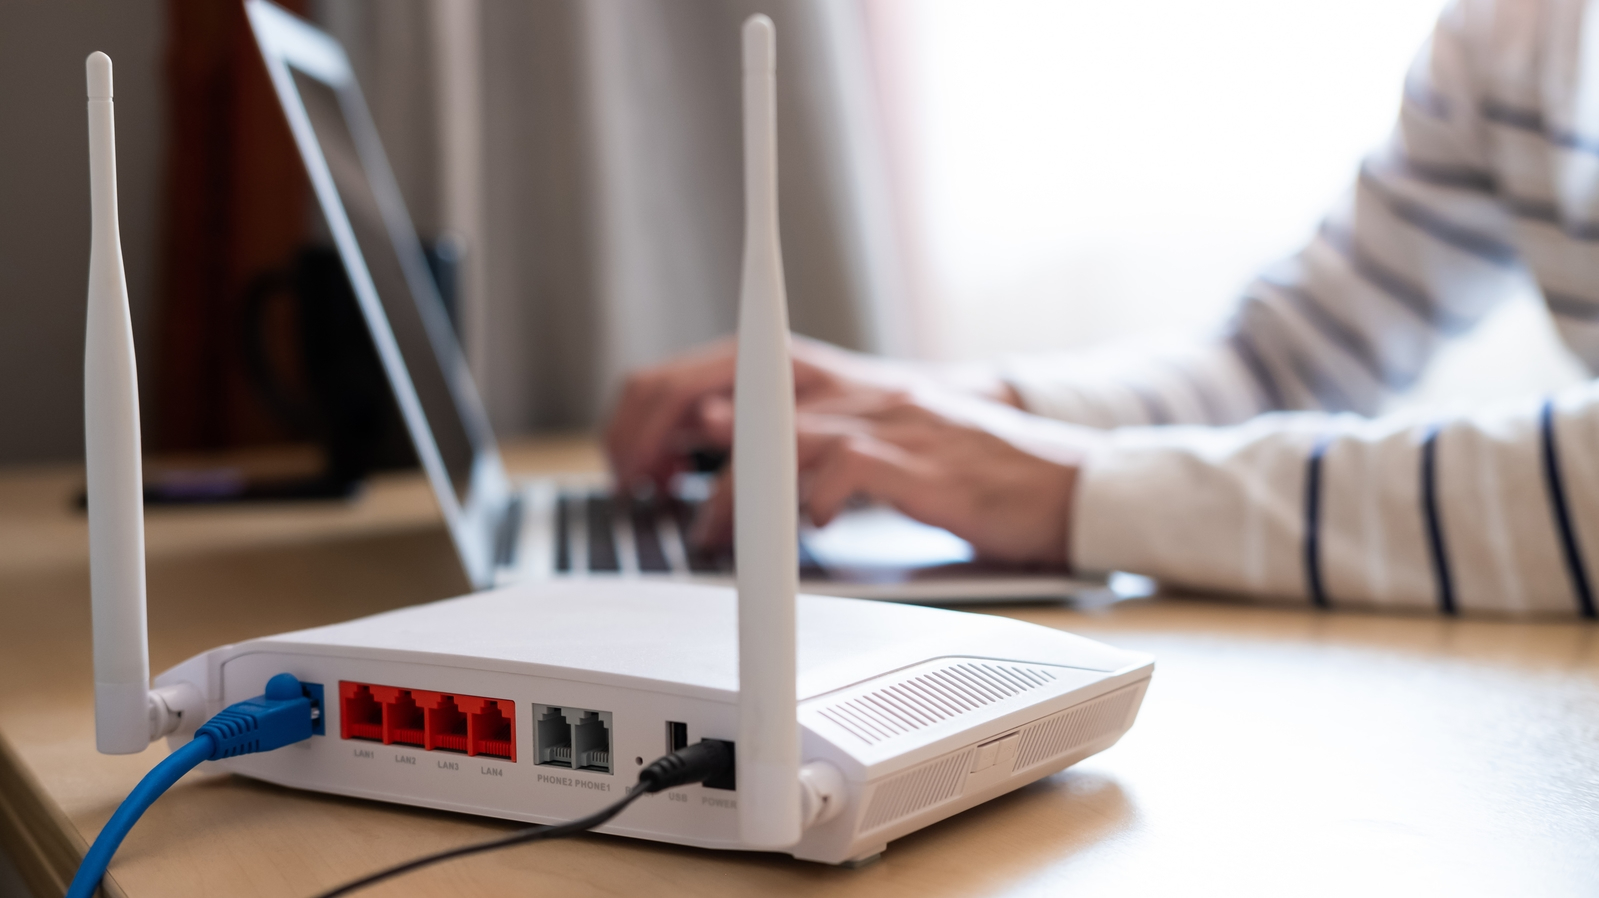
Asus has issued multiple statements regarding a highly publicized botnet attack infecting over 9,000 routers to date. Per our previous reporting, the "AyySSHush" botnet has infected its hosts through a mix of brute-force attacks and authentication bypasses, and hides its backdoor in non-volatile memory, thus attempting to hide from firmware updates and refreshes.
In an official statement regarding the insecurity, Asus told Tom's Hardware that the vulnerabilities can be avoided for those yet uninfected, and fixed for those routers that have been compromised. The hostile agents utilize a known command injection flaw, CVE-2023-39780, to enable SSH access on a custom port (TCP/53282) and insert an attacker-controlled public key for remote access.