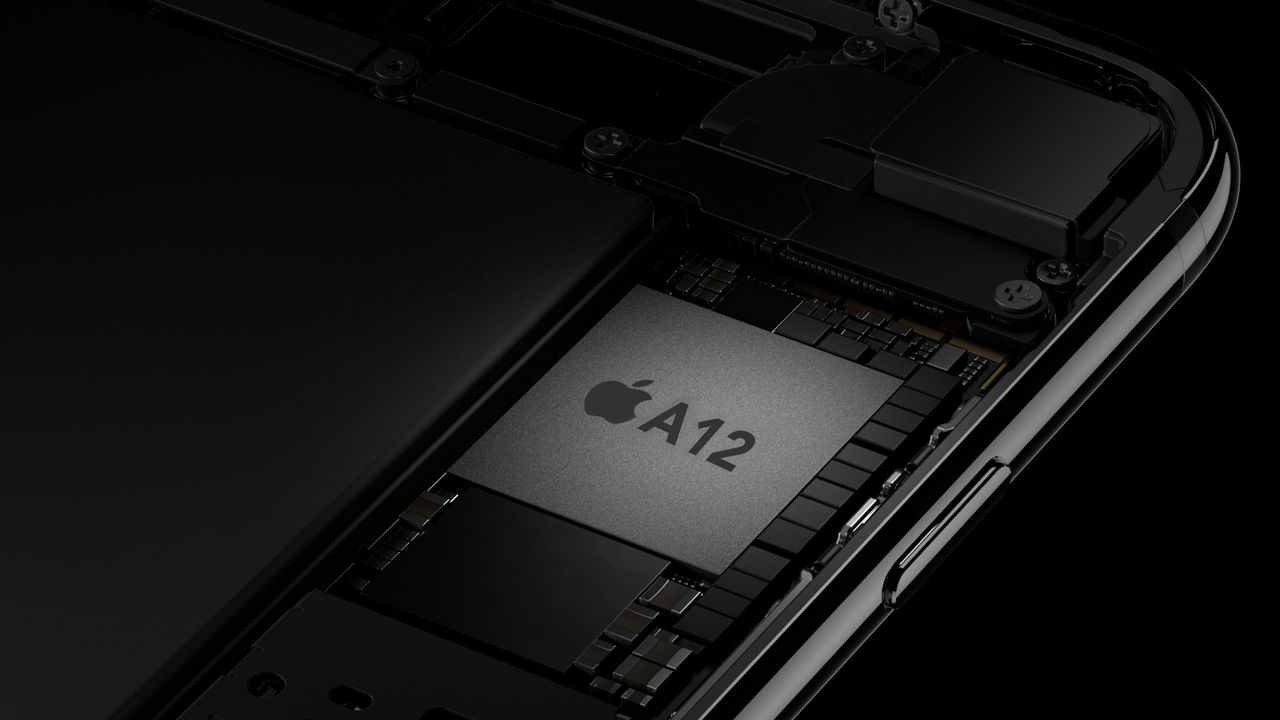
- Paradigm Shift discovered “usbliter8,” a hardware flaw in A12/A13 iPhone and S4/S5 Apple Watch chips allowing jailbreak via USB data handling
- Exploitation requires physical access and Raspberry Pi, but enables bypassing iOS restrictions and deep system compromise
- Apple cannot patch; only unaffected models (pre‑A12 or A14+) are secure, making device replacement the sole mitigation
Security researchers Paradigm Shift have discovered a vulnerability in older iPhone and Apple Watch models which can be used to jailbreak the devices. What makes this vulnerability special is the fact that there is no fix for it - the only way to really be secure is to replace the device with a newer model.