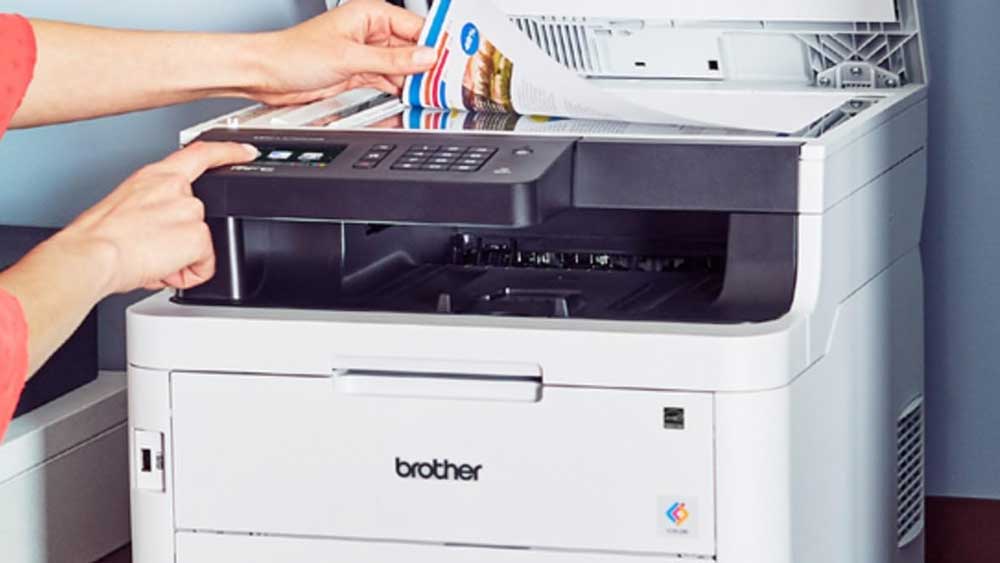
Another reminder to change your devices' default passwords has arrived, thanks to a new critical vulnerability found in Brother printers. 689 different models of Brother printers, plus a handful of other printers from Fujifilm, Toshiba, and Konica Minolta, are susceptible to eight new security vulnerabilities, some of which cannot be patched with firmware updates.
Security company Rapid7 discovered the exploits in a recent investigation of some Brother printers. The most severe of these, CVE-2024-51978, given a 9.8 Critical rating, allows attackers to generate the device's default admin password. The affected models have default passwords created algorithmically using their serial numbers as a seed, so attackers with the printer's serial number (accessible via HTTP thanks to CVE-2024-51977) can create the default password and access the printer and the rest of the network.